Managing Identity and Access Management on Zenconsole
The Identity & Access Management (IAM) feature in Zenconsole allows organization administrators to configure and manage how users authenticate to their organization's Zenarmor deployments.

Figure 1. Identity & Access Management page
By default, Zenconsole Authentication is enabled when a new organization is created, allowing users to authenticate using their Zenconsole credentials without requiring additional configuration.
Organizations can also configure additional authentication methods to integrate with external identity providers and meet their authentication requirements. The availability of these methods may depend on the organization's subscription.
The configured authentication methods apply to both agent-based deployments, including Zenarmor Windows and macOS agents, and agentless deployments, such as gateways and browser-based authentication.
With Identity & Access Management, you can:
- Manage Authentication Methods: View the default authentication method and configure additional authentication methods.
- Integrate External Identity Providers: Enable authentication through Google Cloud Identity, Microsoft Entra ID (Azure AD), or compatible SAML 2.0 identity providers.
- Set a Default Authentication Method: Select the primary authentication method for your organization.
- Enforce Periodic Reauthentication: Specify how frequently users must reauthenticate during active sessions through the Zenarmor endpoint application.
To access the Identity & Access Management settings, follow these steps:
- Sign in to Zenconsole.
- Select the organization you want to manage.
- Navigate to Settings → Organization Settings → IAM → Identity & Access Management.
The Identity & Access Management page contains two main sections:
- Authentication Method: Displays configured authentication methods and allows you to add and manage authentication configurations.
- Reauthentication Interval: Allows you to enforce periodic reauthentication and configure how frequently users must verify their identities during active sessions.
Managing Authentication Methods
The Authentication Method section allows organization administrators to view, configure, and manage authentication methods used to access their organization's Zenarmor deployments.
By default, Zenconsole Authentication is available and marked as Default when a new organization is created. Additional authentication methods can be configured based on your organization's requirements and subscription.
One-Time Password support will be available soon.
The availability of additional authentication methods depends on your organization's subscription. Methods that are not supported by your current subscription may appear disabled.
Enabling Google Cloud Identity
To use Google Workspace for identity management in your organization, you must integrate your Zenconsole organization with Google Workspace. This integration automatically synchronizes your organization's users and groups, keeping their information accurate and up to date without manual effort.
You can enable Google Cloud Identity to allow users to authenticate to your organization using their Google Workspace accounts by following the steps below.
-
Login Zenconsole.
-
Select the organization you want to manage.
-
Navigate to the Settings → Organization Settings → IAM → Identity & Access Management page.
-
Go to Authentication Method pane at the top of the page.
-
Click + Add Authentication Method drop-down menu at the top right of the pane. The available authentication methods will appear.

Figure 2. Selecting Authentication Method
-
Click Google Cloud Identity option to configure Google Workspace as the organization authentication method. This will pop up the Google Cloud Identity configuration wizard window.
-
Type the domain that you want to be synchronized with Zenconsole for user authentication. Users with email addresses from these domains can sign in to your organization.
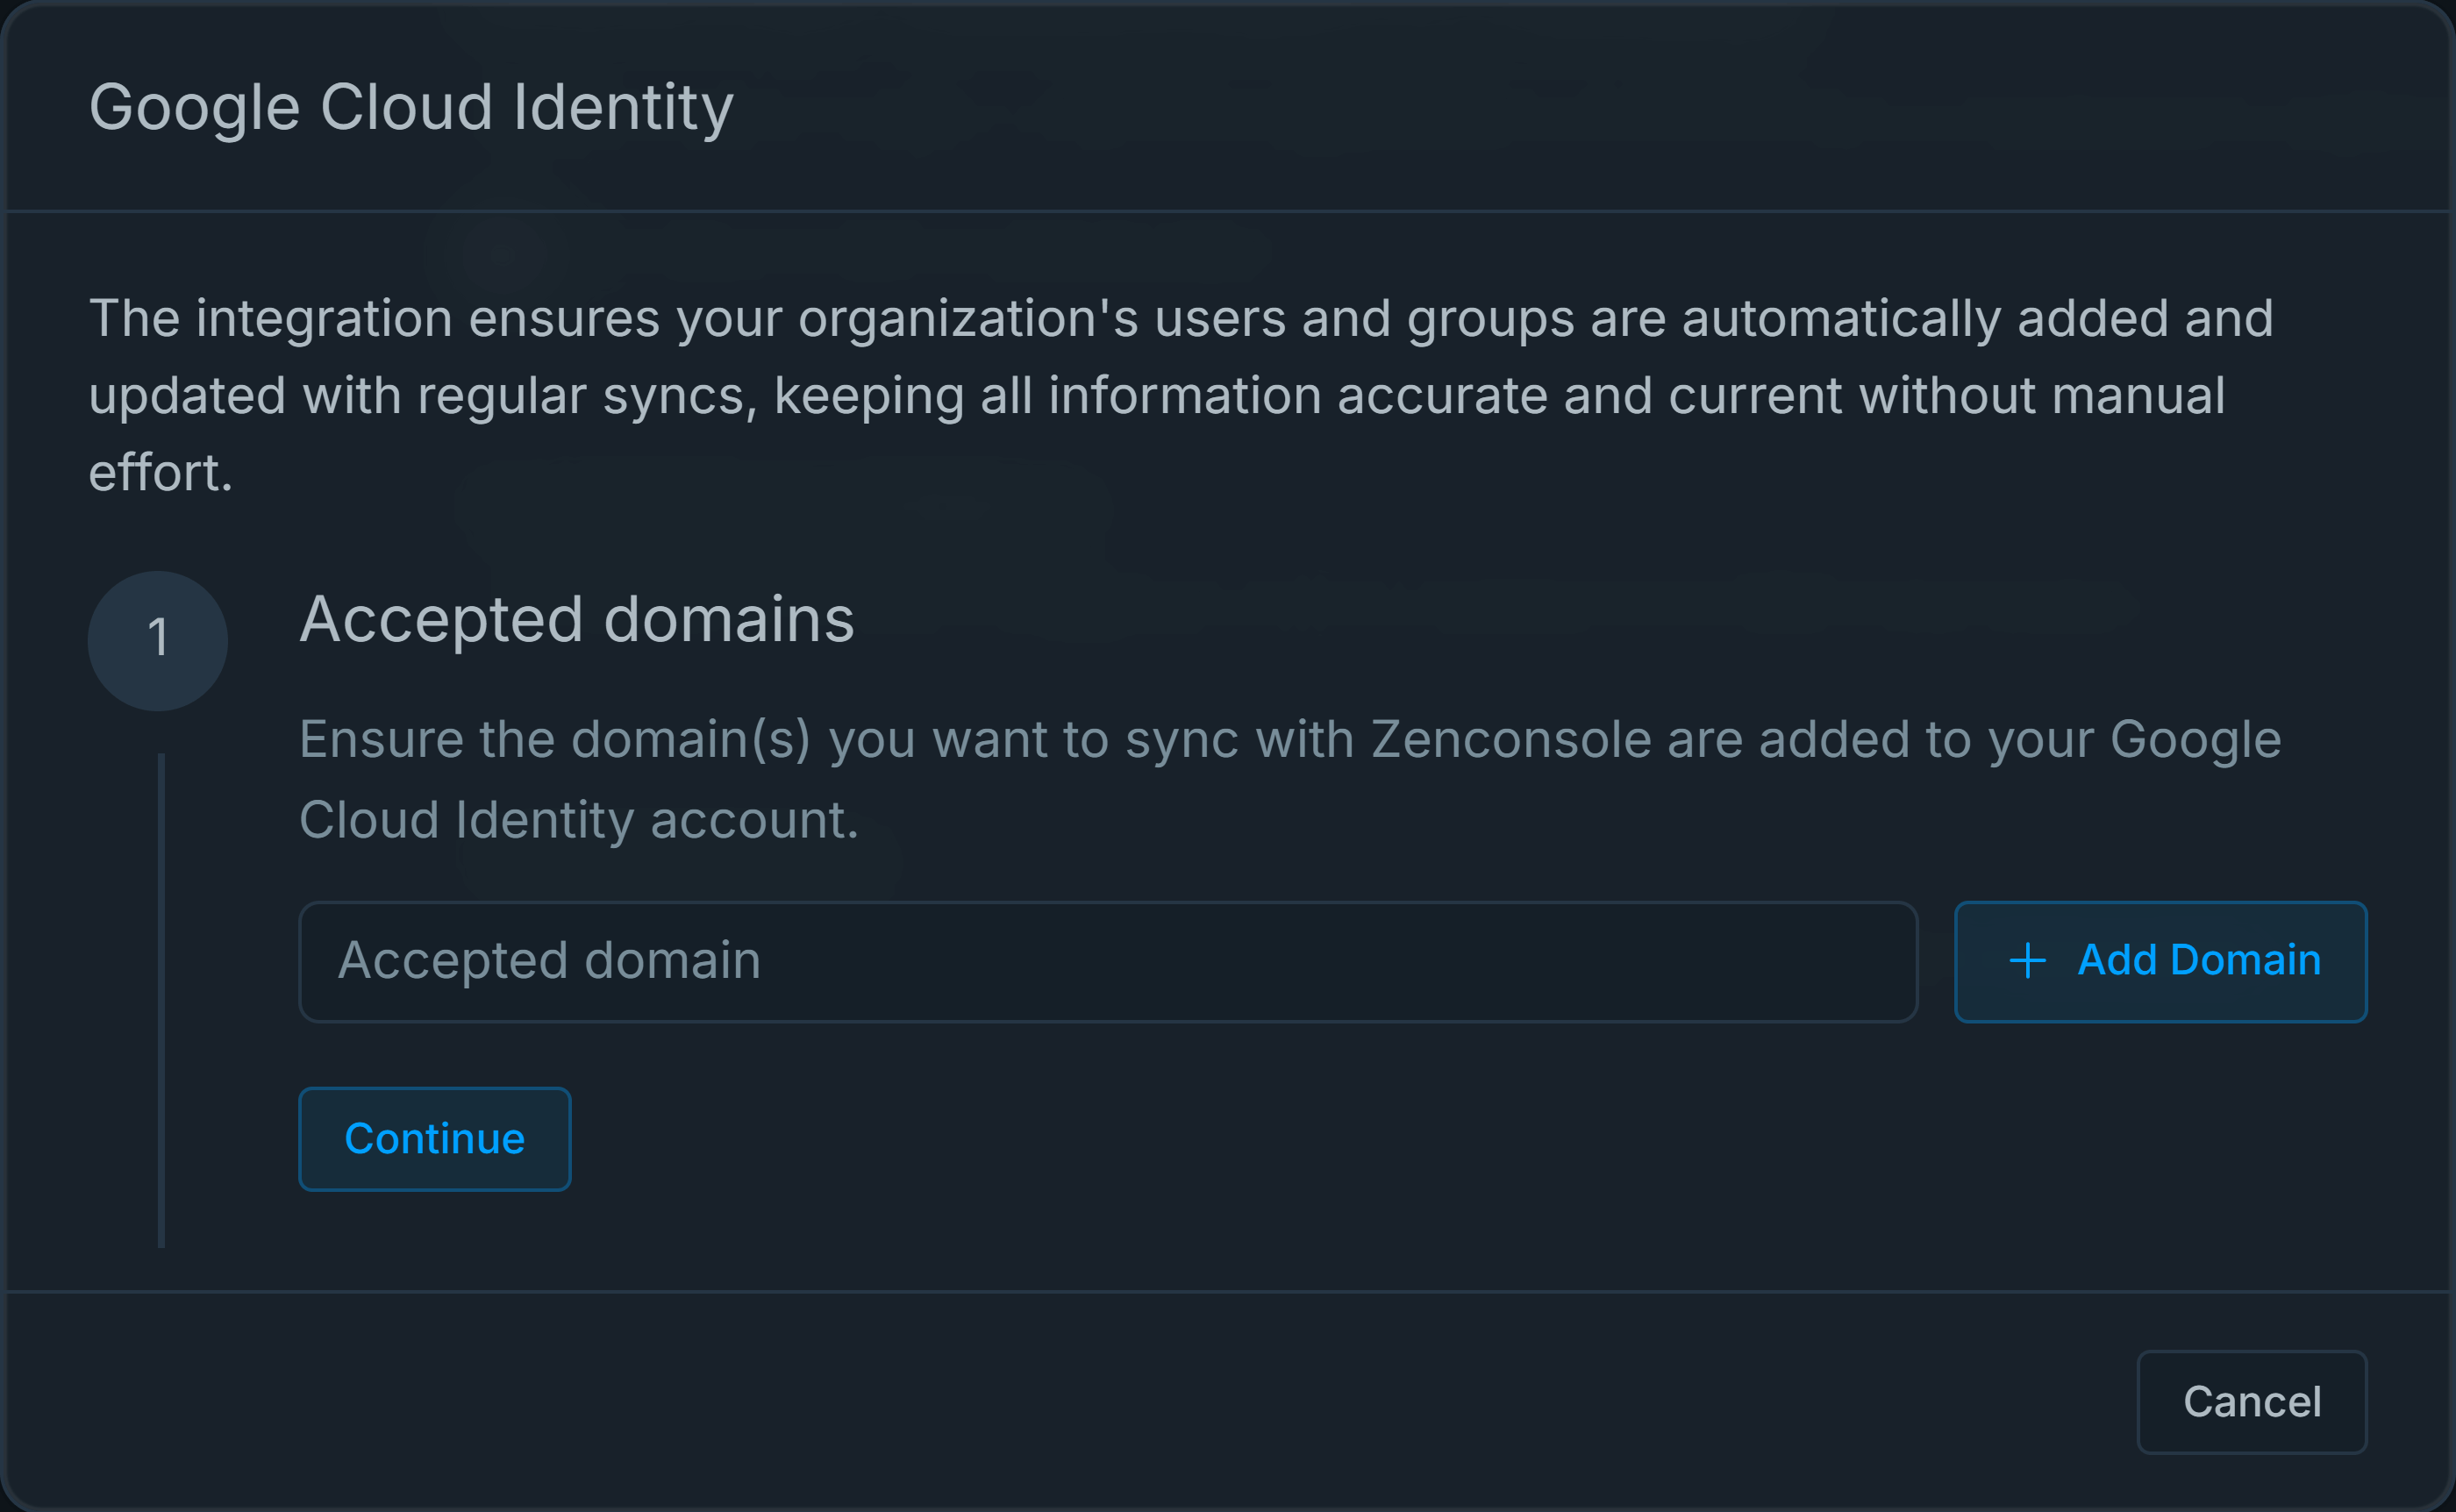
Figure 3. Adding Accepted Domains
-
Click + Add Domain button. You may add as many domains as you need. Accepted domains will be automatically displayed below. You may quickly remove them by clicking the
xicon next to the domain name if you need.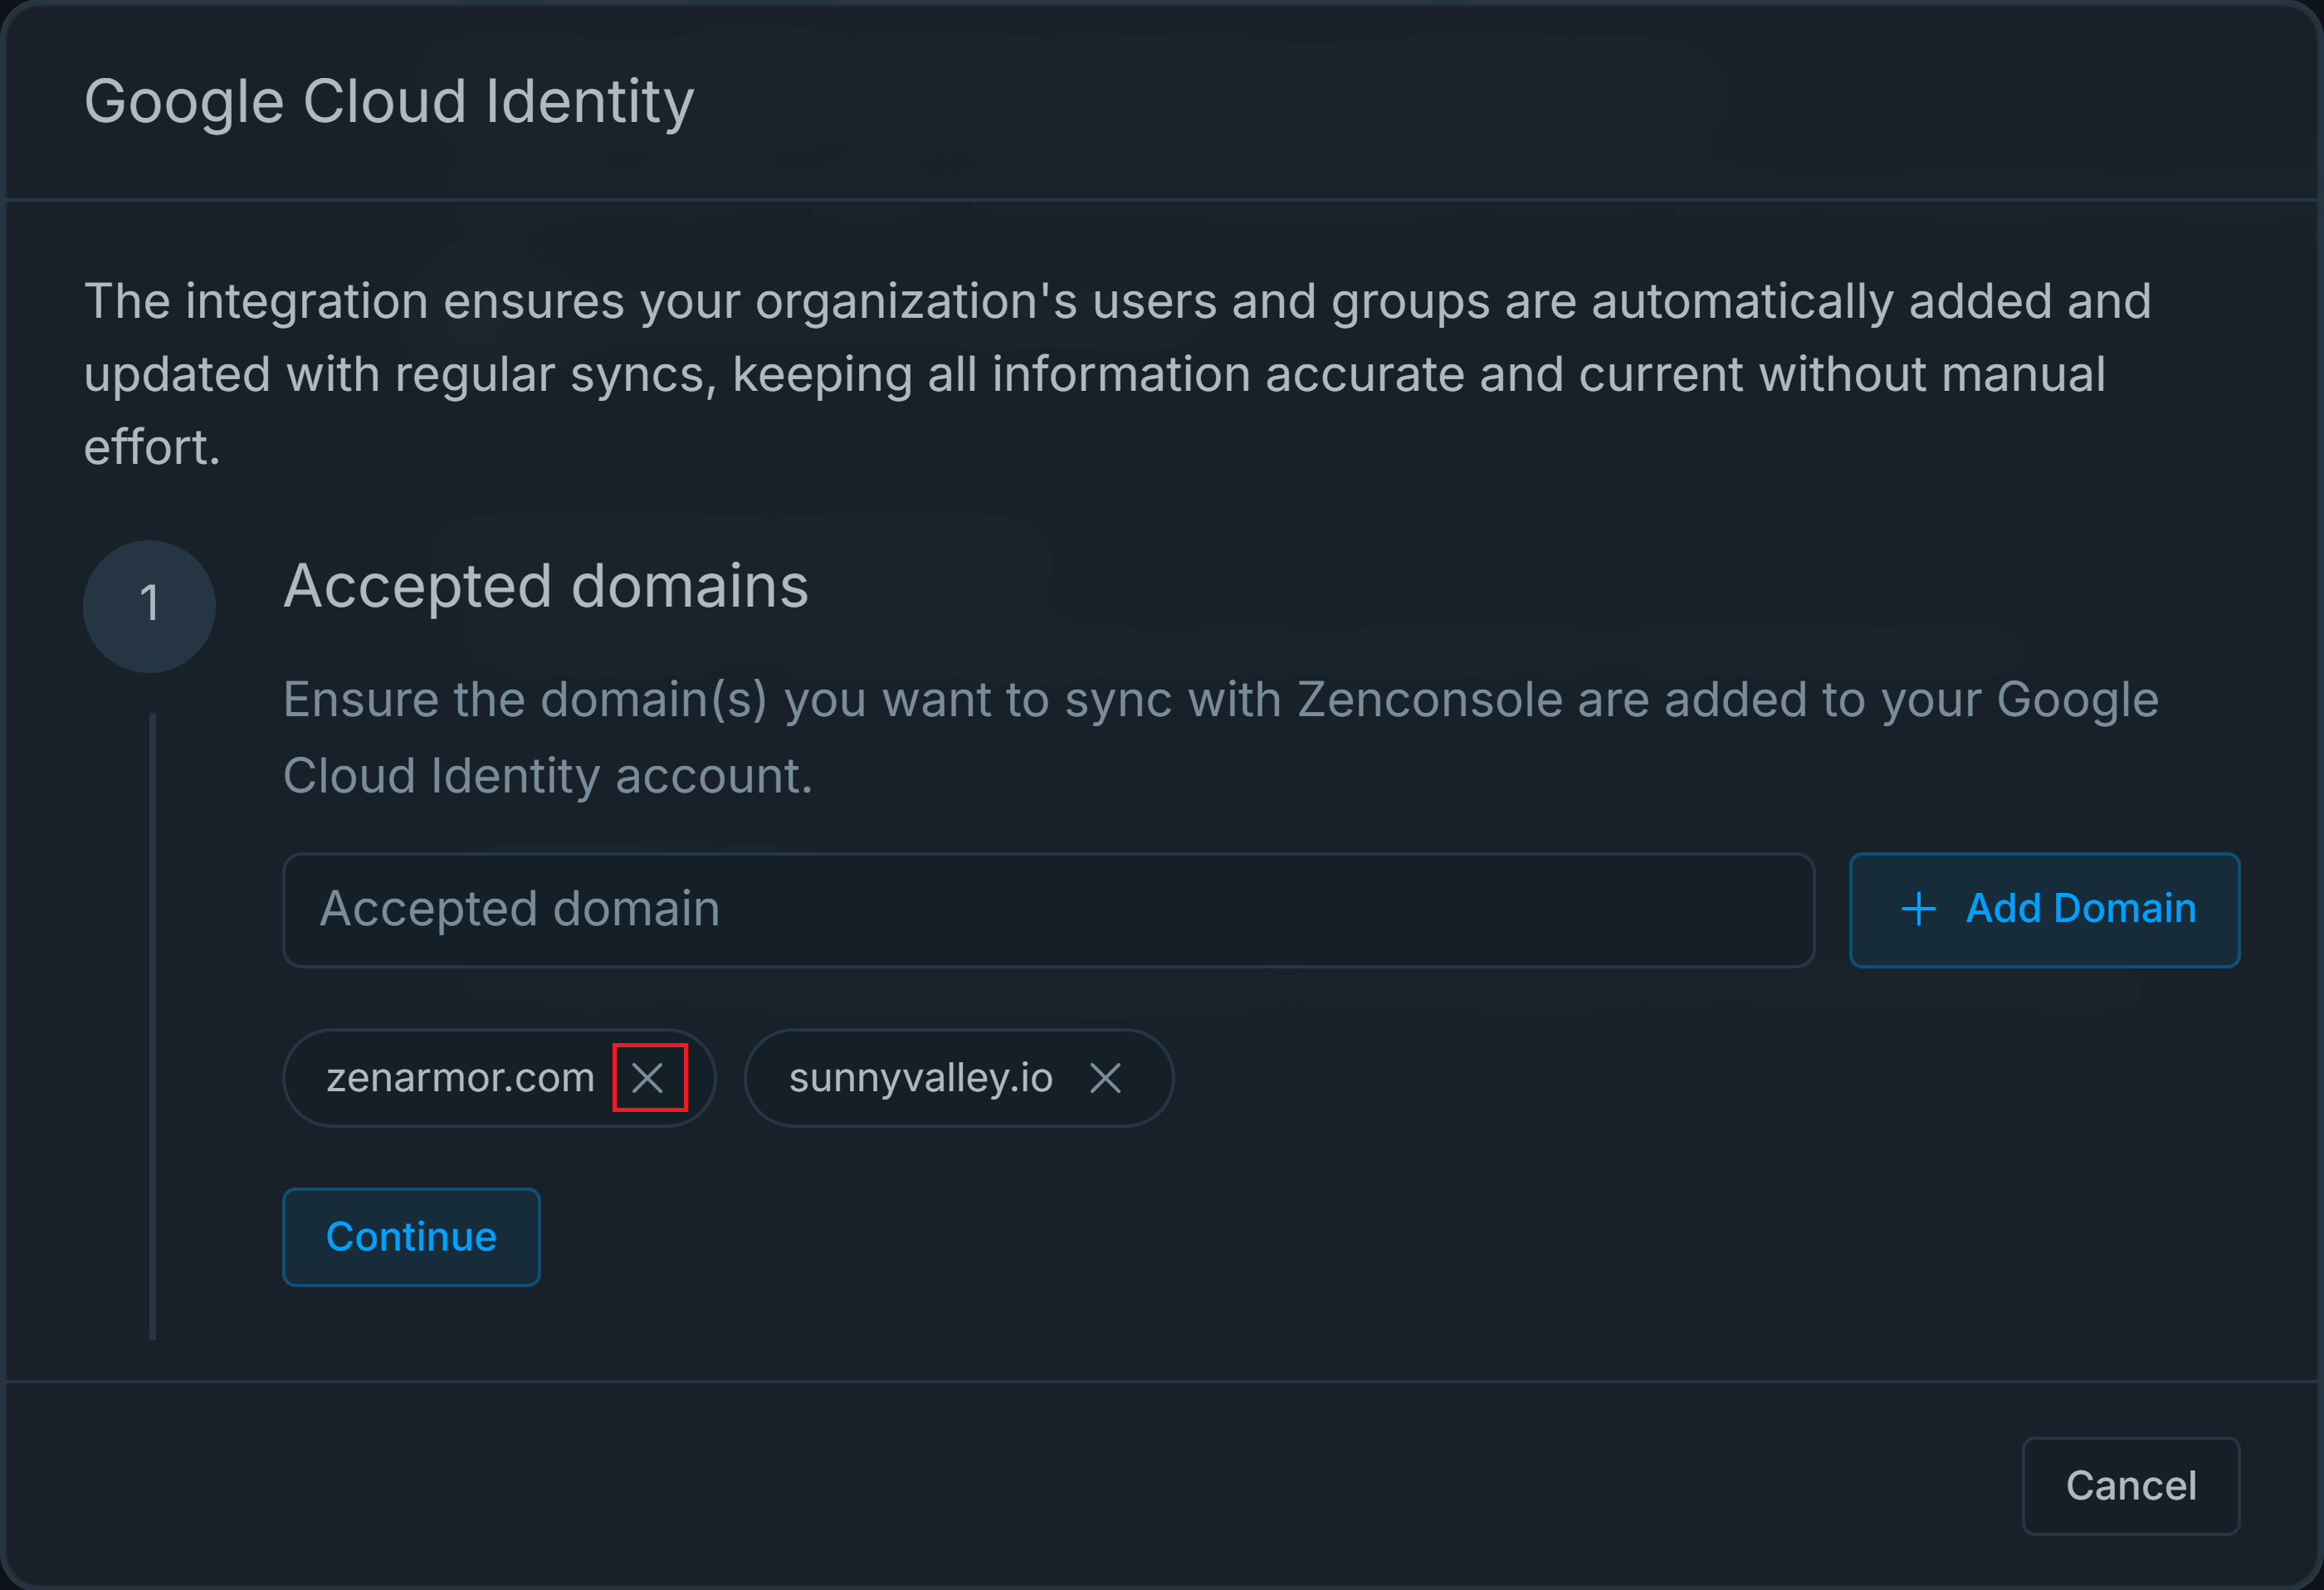
Figure 4. Accepted Domains
-
Click Continue to proceed with the Google Cloud Identity configuration. This will provide a link for the Google Cloud Identity integration and await authorization from your domain administrator.
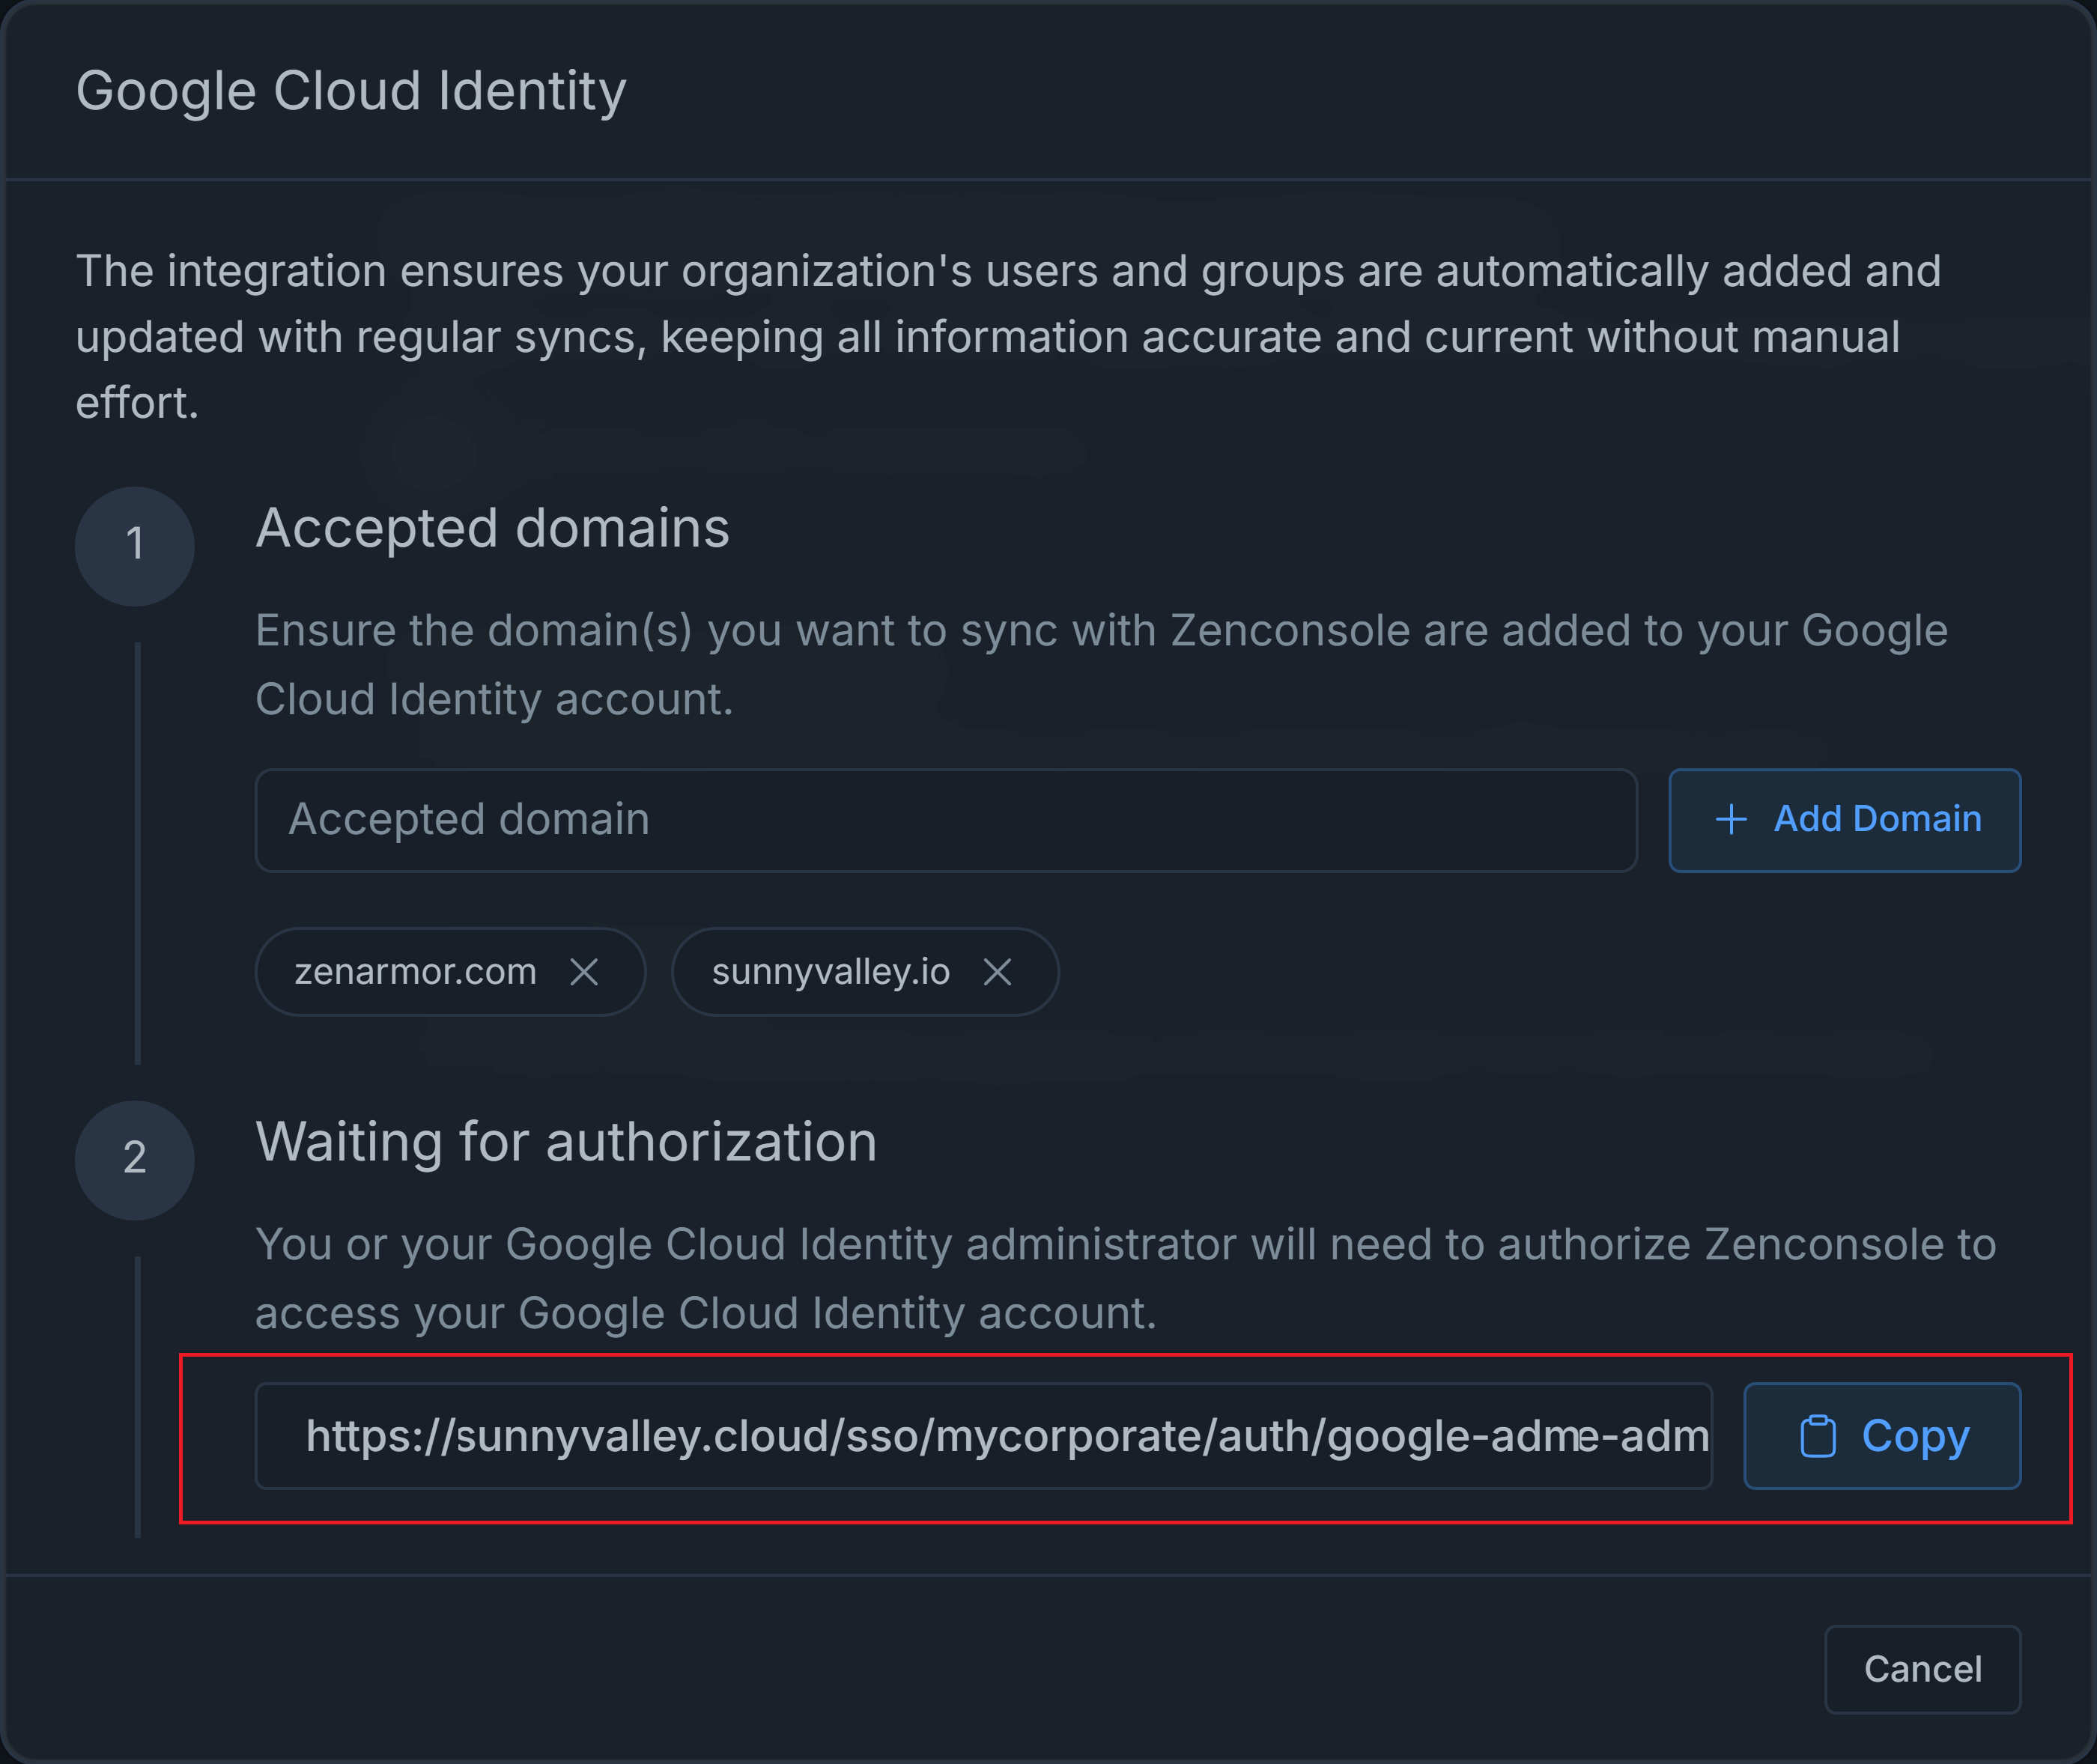
Figure 5. Generating Link and Waiting for Google IDP Authorization
-
You may either click on the link if you have administrator privileges for your domain or copy it to share it with domain administrators. So that Zenconsole will be able to access your Google Workspace and synchronize with user accounts.
-
Go to the link generated in the previous step and sign in to Google using an account with admin privileges.
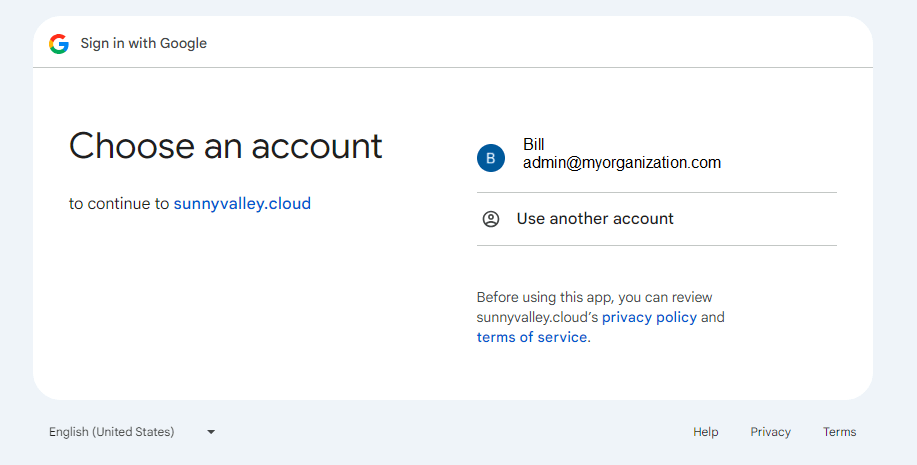
Figure 6. Signin Google with Admin Account
-
Click Allow to give the required privileges on your domain to Zenconsole.

Figure 7. Accepting Permission Requests
-
You should observe that Zenconsole access has been granted to your domain. Zenconsole will now routinely update your users and groups, as they are now synchronized.

Figure 8. Google Access Granted
-
Click on the Zenconsole link which will redirect you to the organization Identity & Access Management page. You should now see Google Cloud Identity in the Authentication Method list.
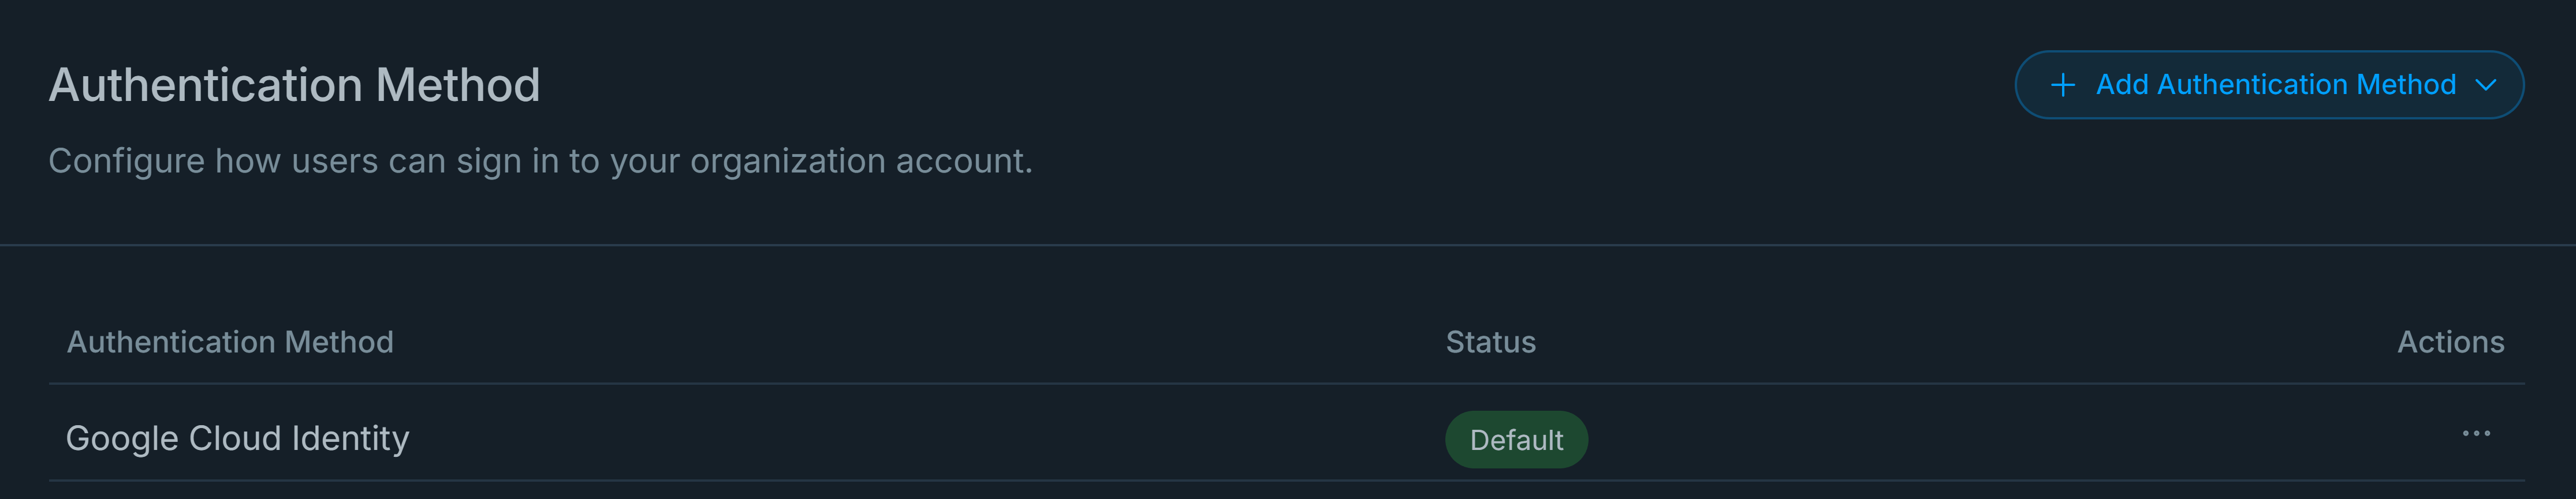
Figure 9. Google Default Authentication Method
Beware that to let your domain users sign in to the organization, you will need to approve them by navigating to the Users settings page.
Enabling Generic SAML 2.0
You can use any identity provider (IdP) that supports the SAML 2.0 single sign-on (SSO) authentication protocol, such as Google Workspace or Auth0, to authenticate users in your organization.
To configure Generic SAML 2.0 authentication, you need to:
- Select an identity provider that supports SAML 2.0.
- Create a SAML application in your identity provider and download its metadata file.
- Import the SAML IdP metadata file into your Zenconsole organization.
The following sections explain how to create and download SAML 2.0 IdP metadata using Google Workspace and Auth0, and how to import the metadata into Zenconsole.
When using Generic SAML 2.0 authentication, you must manually add users and groups to your Zenconsole organization. Unlike Google Cloud Identity integration, Generic SAML 2.0 authentication does not automatically synchronize users and groups.
Creating SAML2 IdP Metadata using Google Workspace
You may easily create an application and download IdP metadata on Google Workspace for your organization by following these steps:
-
Sign in to your Google Admin console.
-
In the Admin console, Navigate to Apps > Web and mobile apps on the left-side bar.
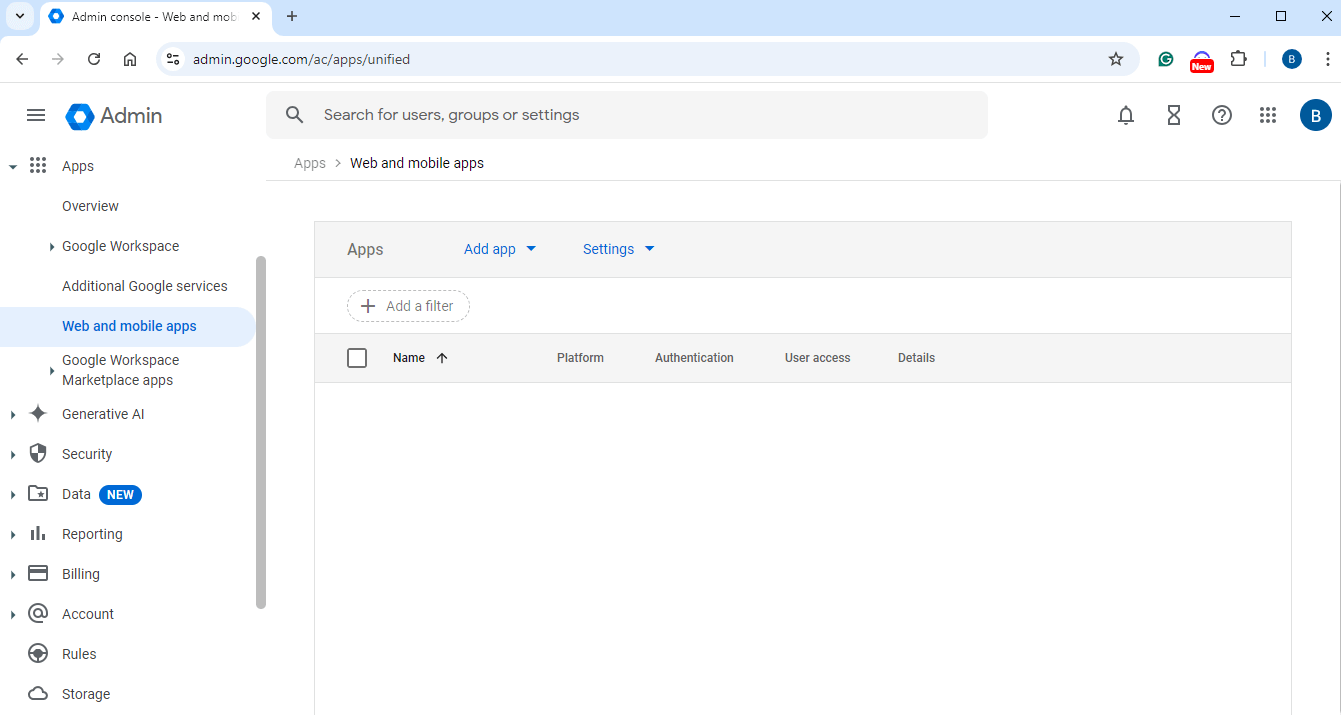
Figure 10. Google Web and Mobile Apps
-
Click Add app drop down menu and then select Add custom SAML app.
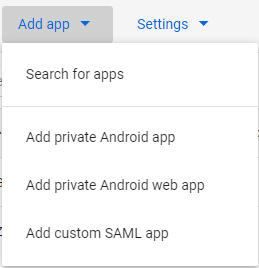
Figure 11. Adding Custom SAML App
-
Enter App Name, such as
Zenarmor. -
Optionally you may type Description and add an icon for the app.
-
Click Continue.
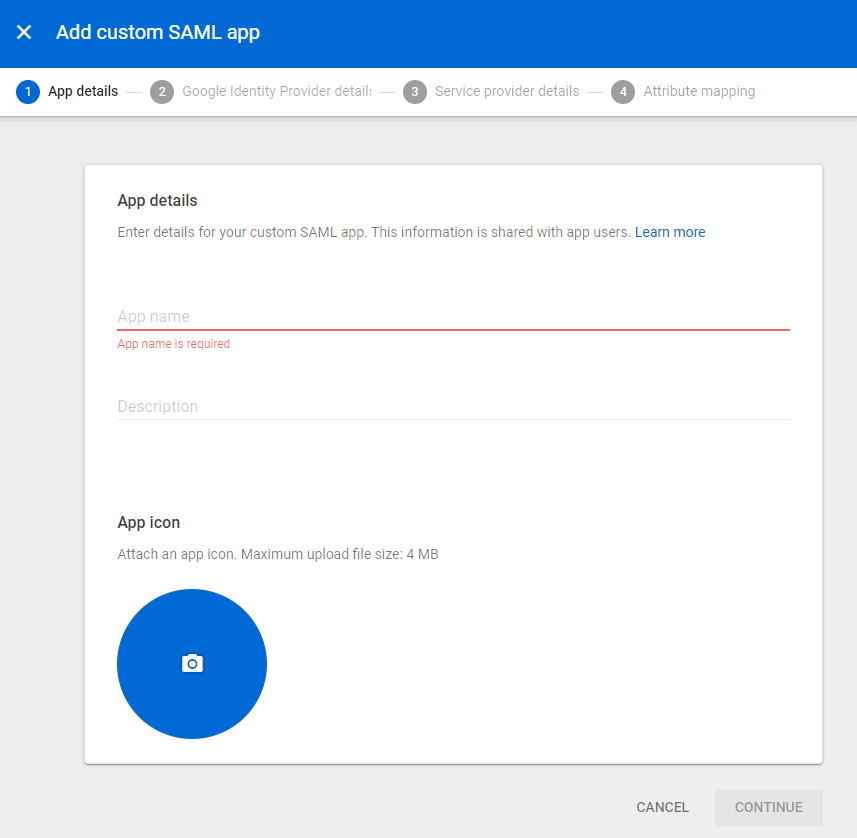
Figure 12. Google SAML App Details
-
Click Download Metadata button to download the IdP metadata file.

Figure 13. Downloading Google IDP Metadata
-
Click on the Save button to download the Google iDP metadata file in
xmlformat to your local disk. -
Click Continue.
-
Enter ACS URL, such as
https://dash.zenarmor.com/saml/{domain}. -
Enter Entity ID, such as
https://dash.zenarmor.com/saml/{domain} -
You may leave Name ID format and Name ID as default.

Figure 14. Google iDP Service Provider Details
-
Click Continue.
-
You may skip Attribute Mapping settings and, click Finish.
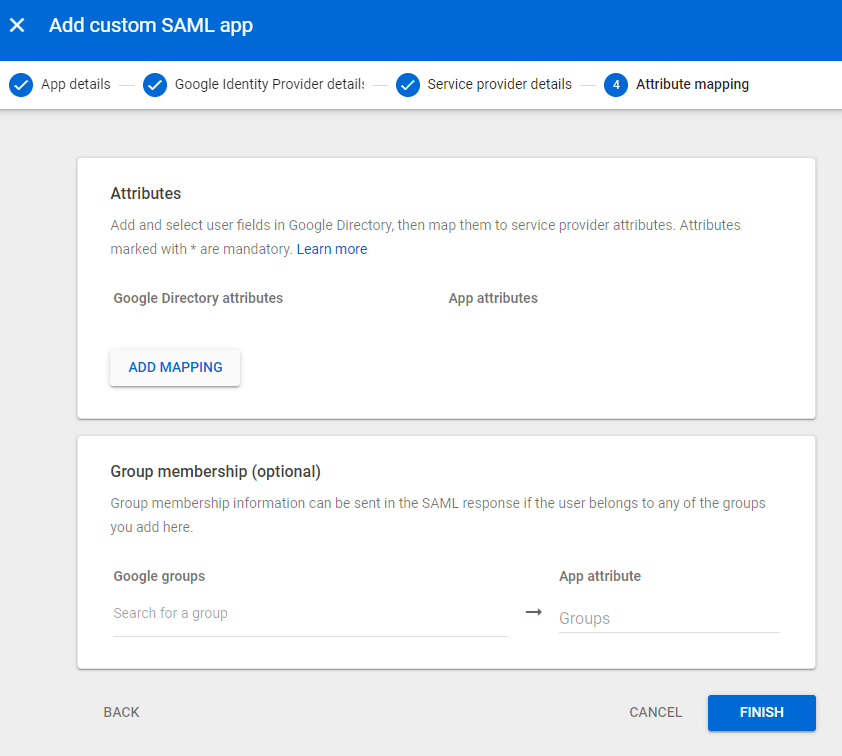
Figure 15. Google Attribute Mapping
-
Click on the User access pane.
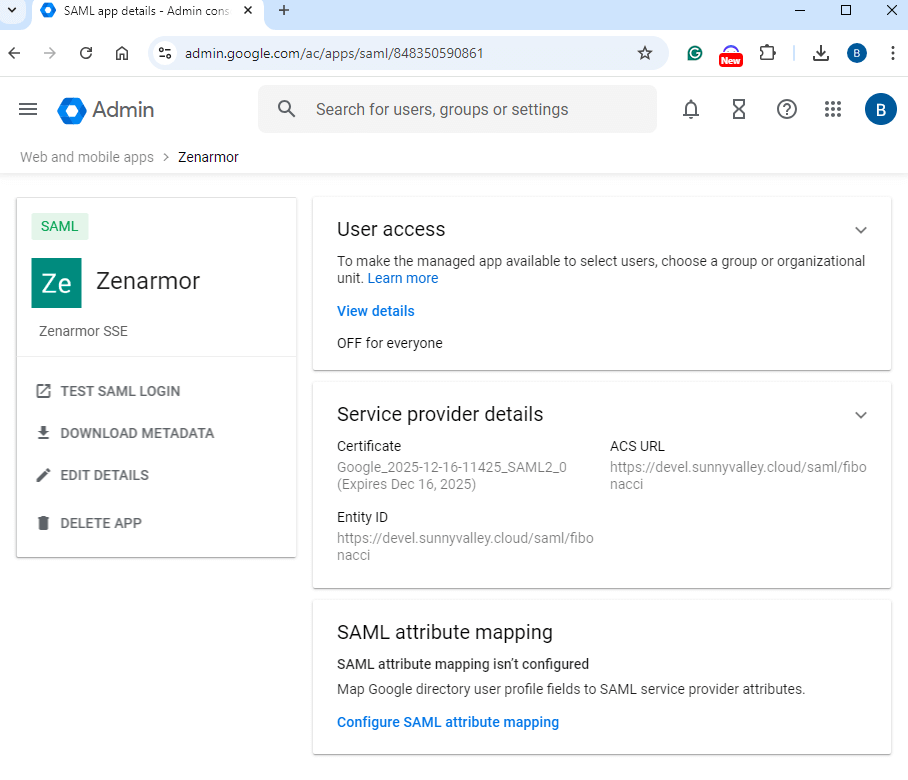
Figure 16. Google view saml conf
-
Set Service status to ON for Everyone.
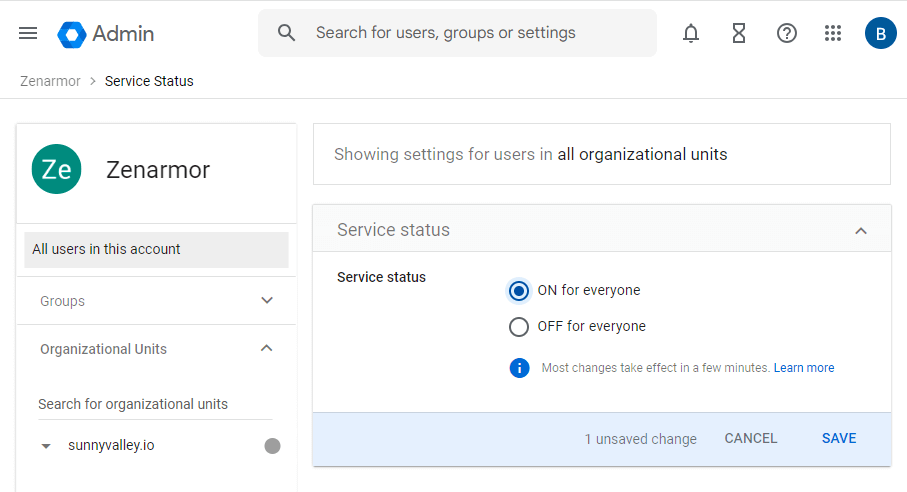
Figure 17. Setting Google Service Status
-
Click Save to activate settings.
Your Google IdP SAML 2.0 configuration is ready to use.
Creating SAML2 IdP Metadata using Okta
You may easily create an application and download IdP metadata on Okta for your organization by following these steps:
-
Sign in to your Auth0.
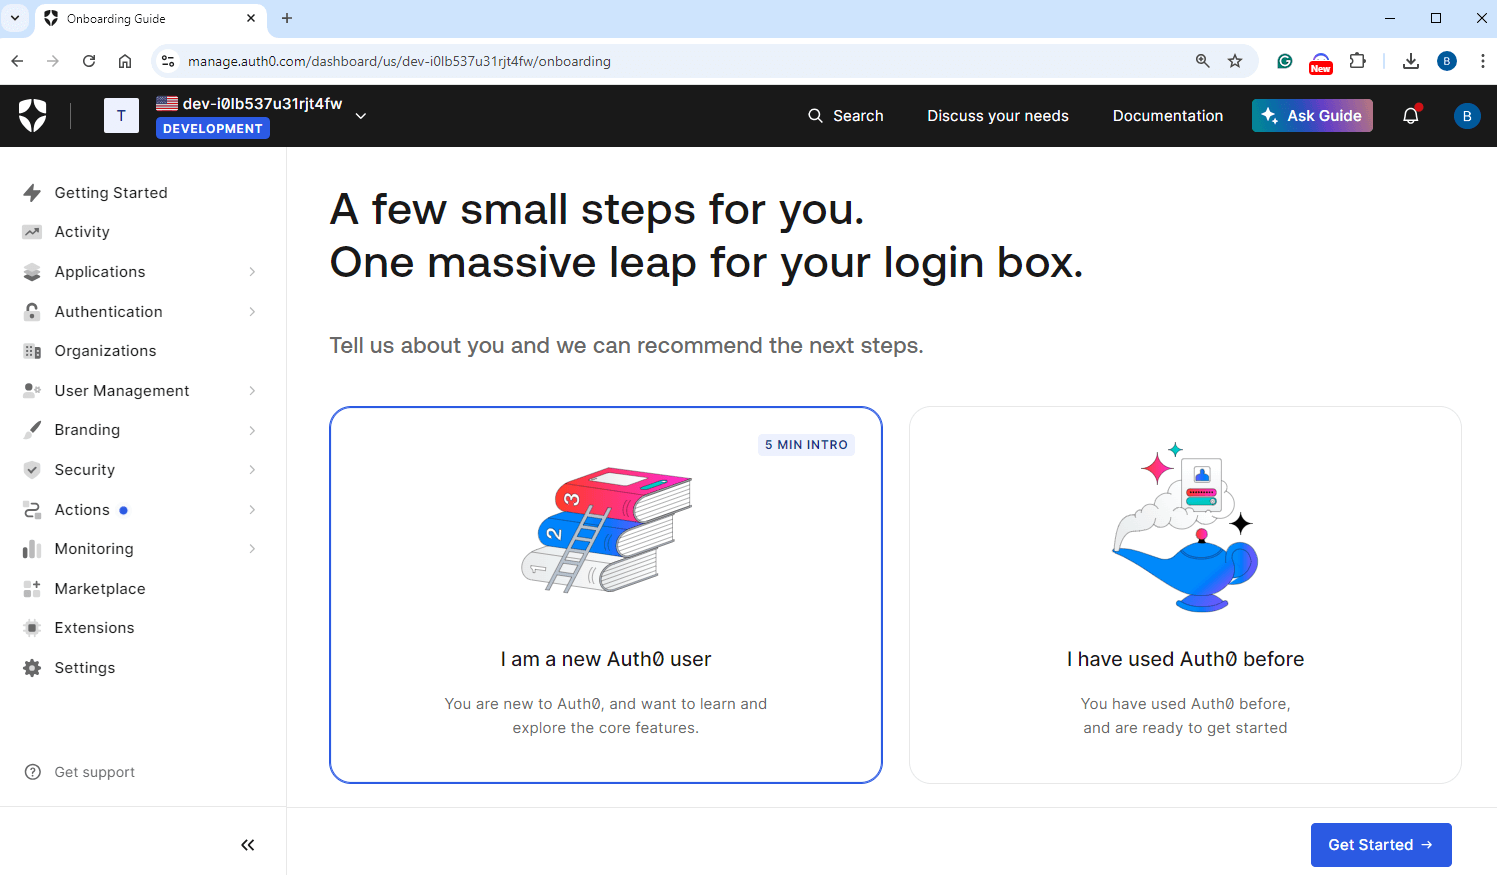
Figure 18. Auth0 Dashboard
-
Navigate to the Applications > Applications on the left-side bar.
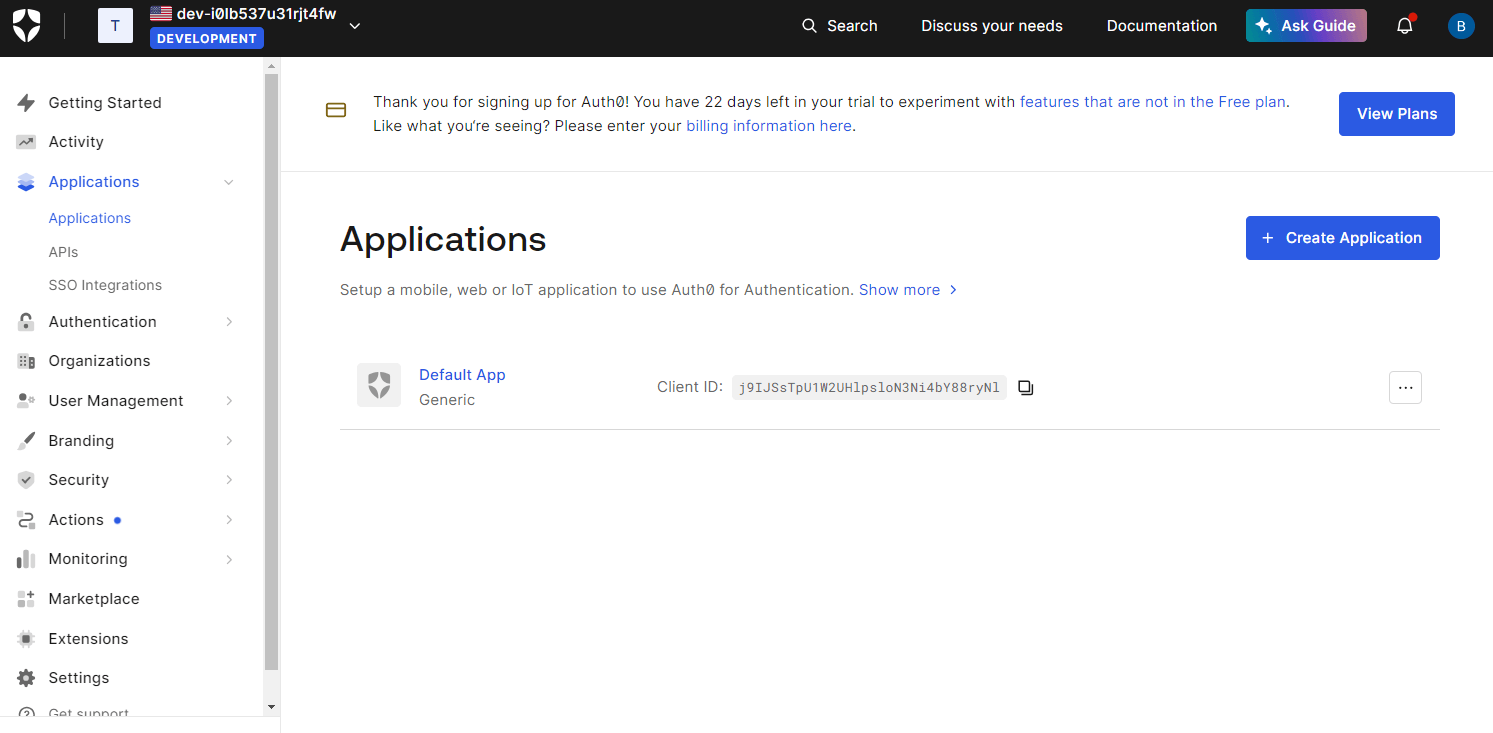
Figure 19. Navigate Applications
-
Click + Create Application to add an application.
-
Enter Name, such as Zenarmor and then click Create. You may leave the Application Type option as Native, default. This will automatically create your app.
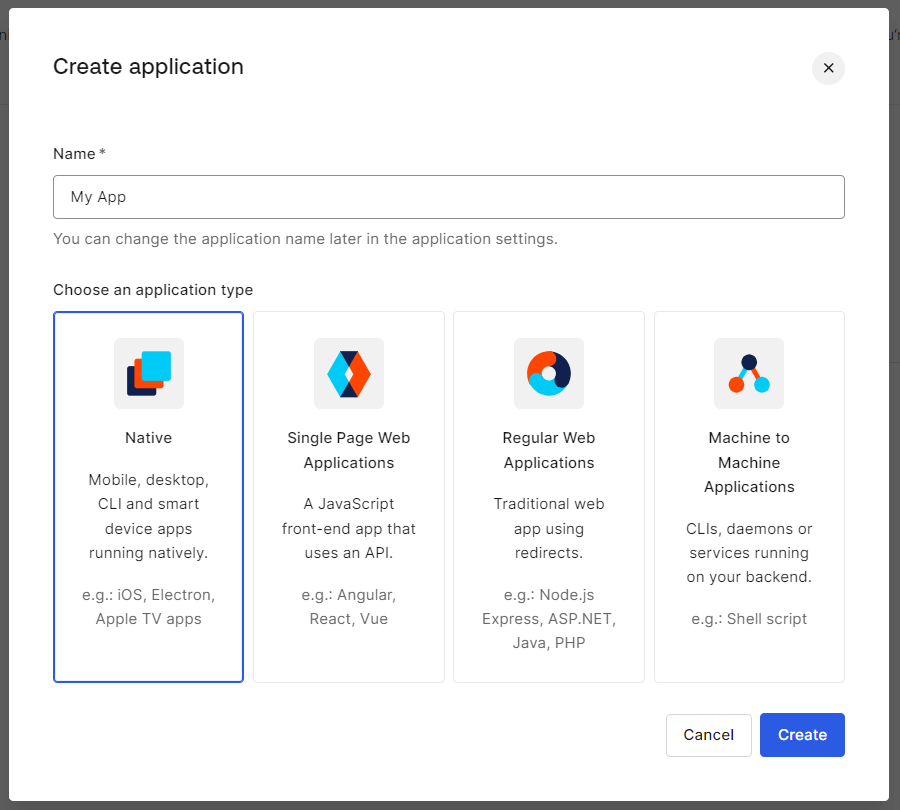
Figure 20. Naming Application
-
Go Addons tab on your new application dashboard.
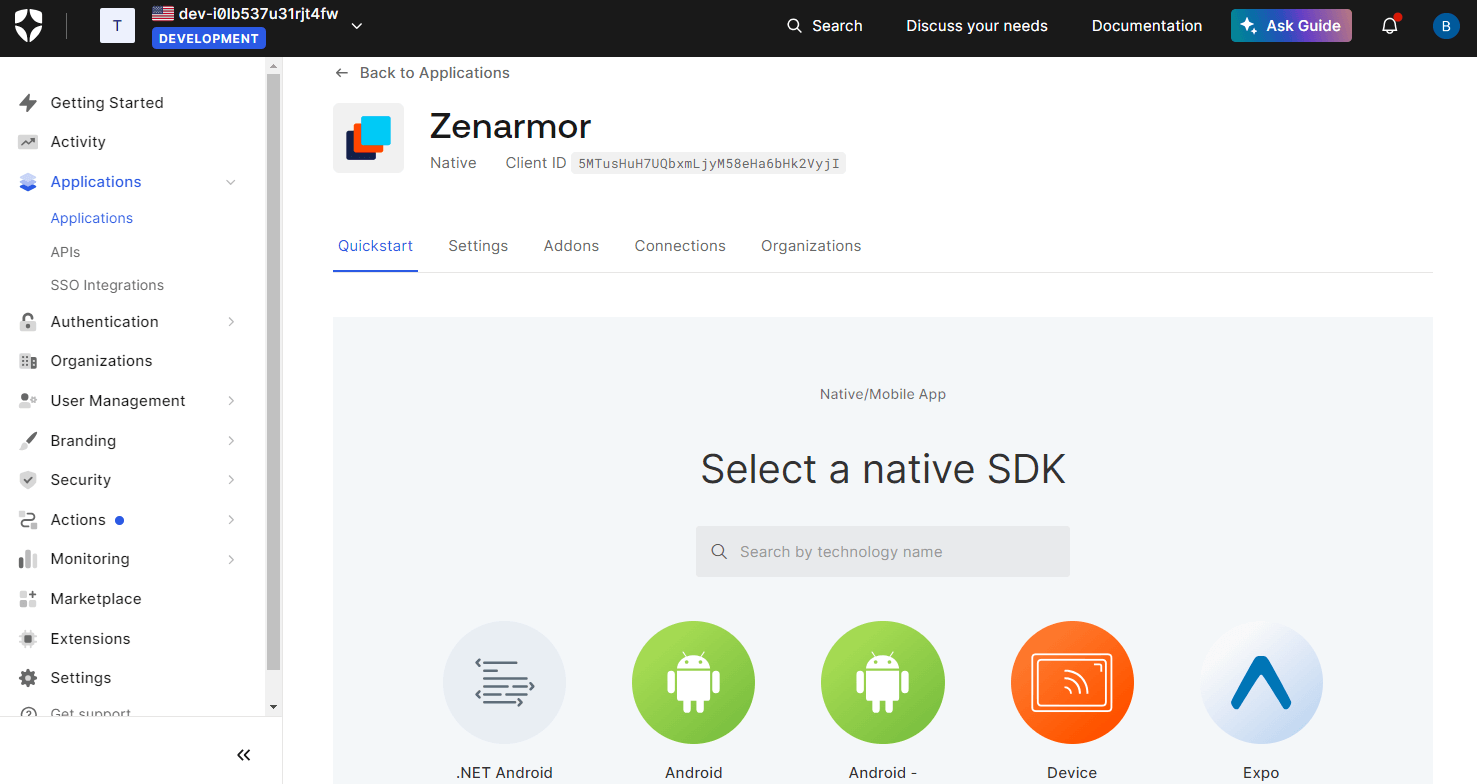
Figure 21. App Dashboard
-
Enable SAML2 WEB APP by clicking on the toggle bar. This will launch the SAML2 Web App Addon window.
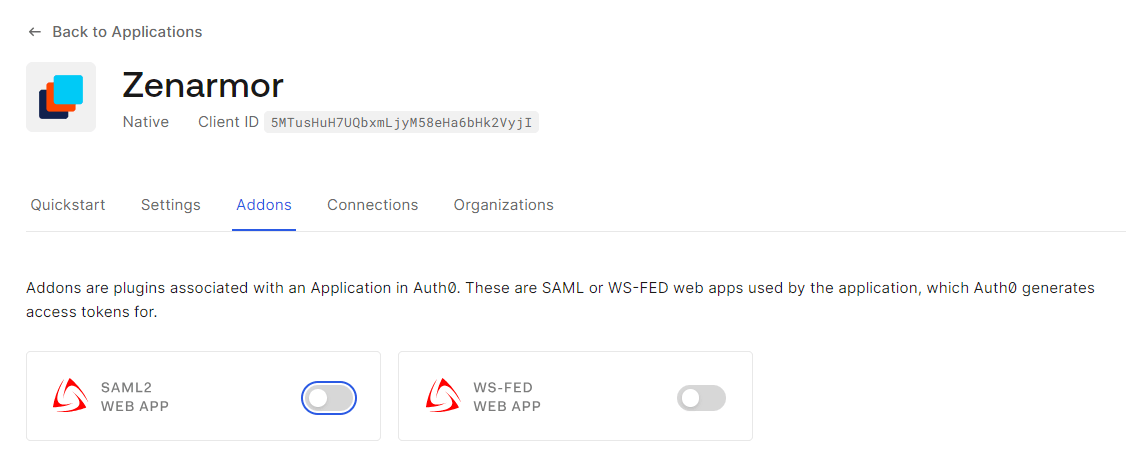
Figure 22. Enabling SAML2 WEB APP
-
Click on Download link next to Identity Provider Metadata in the SAML2 Web App Addon Usage tab.
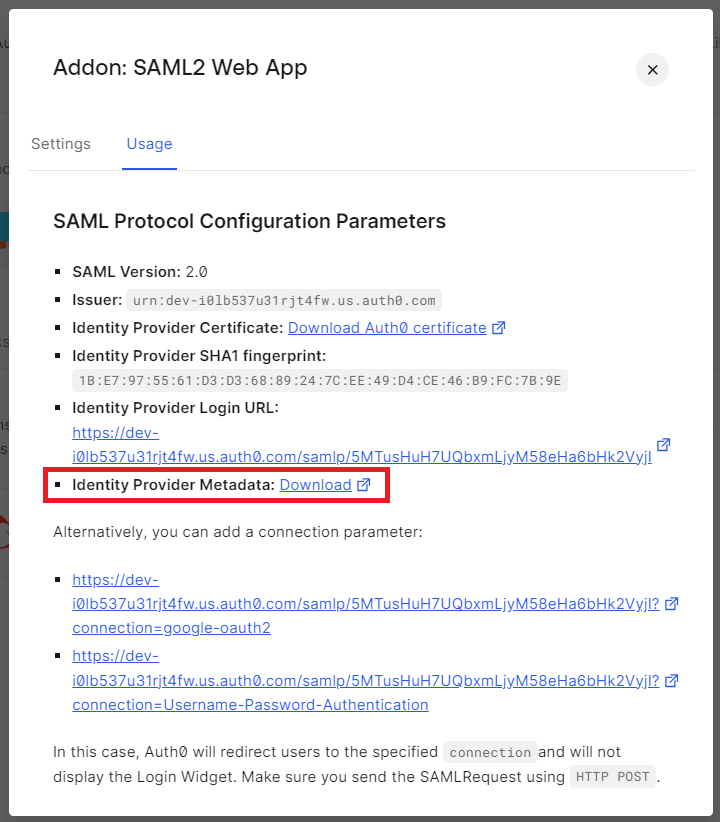
Figure 23. SAML2 Web App Addon Usage
-
Click on the Save button to download the iDP metadata file to your local disk.
-
Navigate to Settings tab in the SAML2 Web App Addon window.
-
Enter Application Callback URL, such as
https://dash.zenarmor.com/saml/{domain}.
Figure 24. Setting Application Callback URL
-
Navigate to the bottom of the window and then click Enable.
-
Close SAML2 Addon.
-
Navigate to the Settings tab.

Figure 25. App Settings
-
Scroll down to the Application URIs section.

Figure 26. Updating Application URI
-
Enter Application Login URI, such as
https://dash.zenarmor.com/saml/{domain}. -
Enter Allowed Callback URLs, such as
https://dash.zenarmor.com/saml/{domain}. -
Enter Allowed Web Origins, such as https://dash.zenarmor.com.
-
Click Save Changes to activate settings.
Importing SAML 2 IdP Metadata on Zenconsole
To complete SAML2 authentication configuration, you may quickly import your SAML 2.0 IdP metadata file you have recently created on the identity provider IdP website into the Zenconsole by following the next steps.
-
Login Zenconsole.
-
Select the organization that you have recently created.
-
Navigate to the Settings → Organization Settings → IAM → Identity & Access Management.
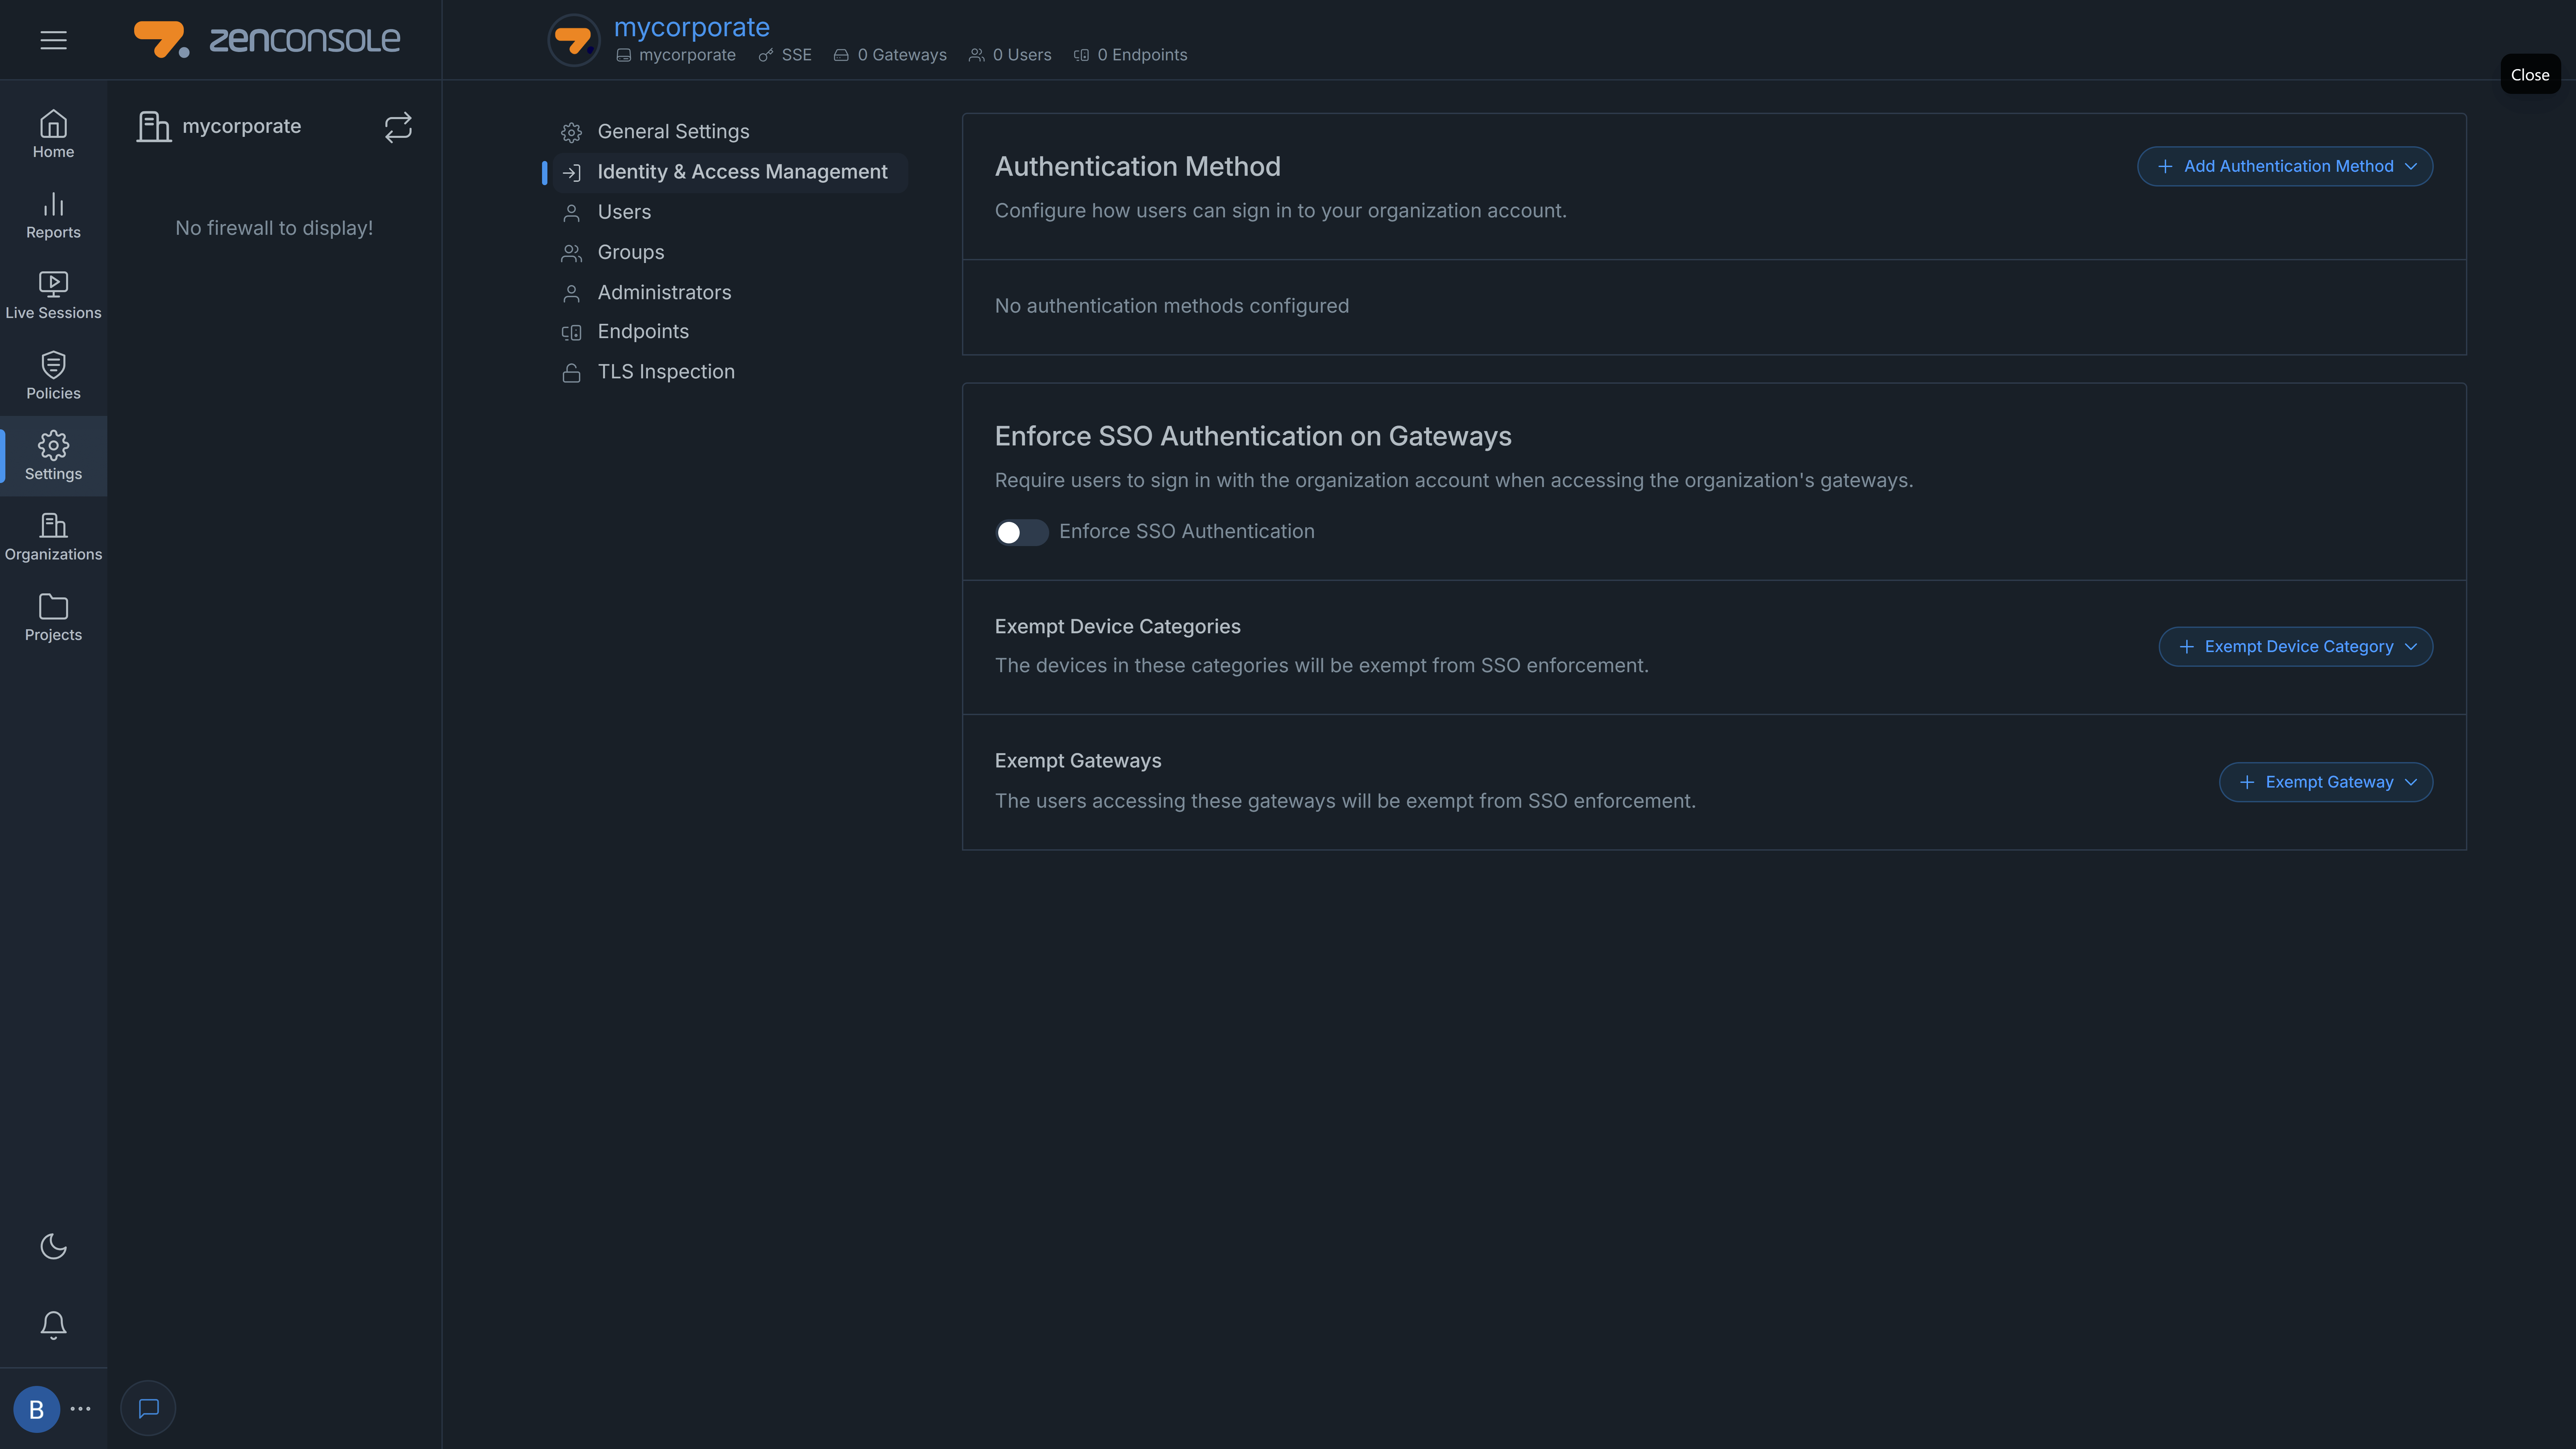
Figure 27. Identity Access Management Settings Page
-
Go to Authentication Method pane at the top of the page.
-
Click + Add Authentication Method drop-down menu at the top right of the pane. All supported authentication methods will appear.

Figure 28. Selecting Authentication Method
-
Click Generic SAML 2.0 menu to configure the SAML 2.0 protocol as the organization authentication method. This will open the SAML 2.0 configuration window.
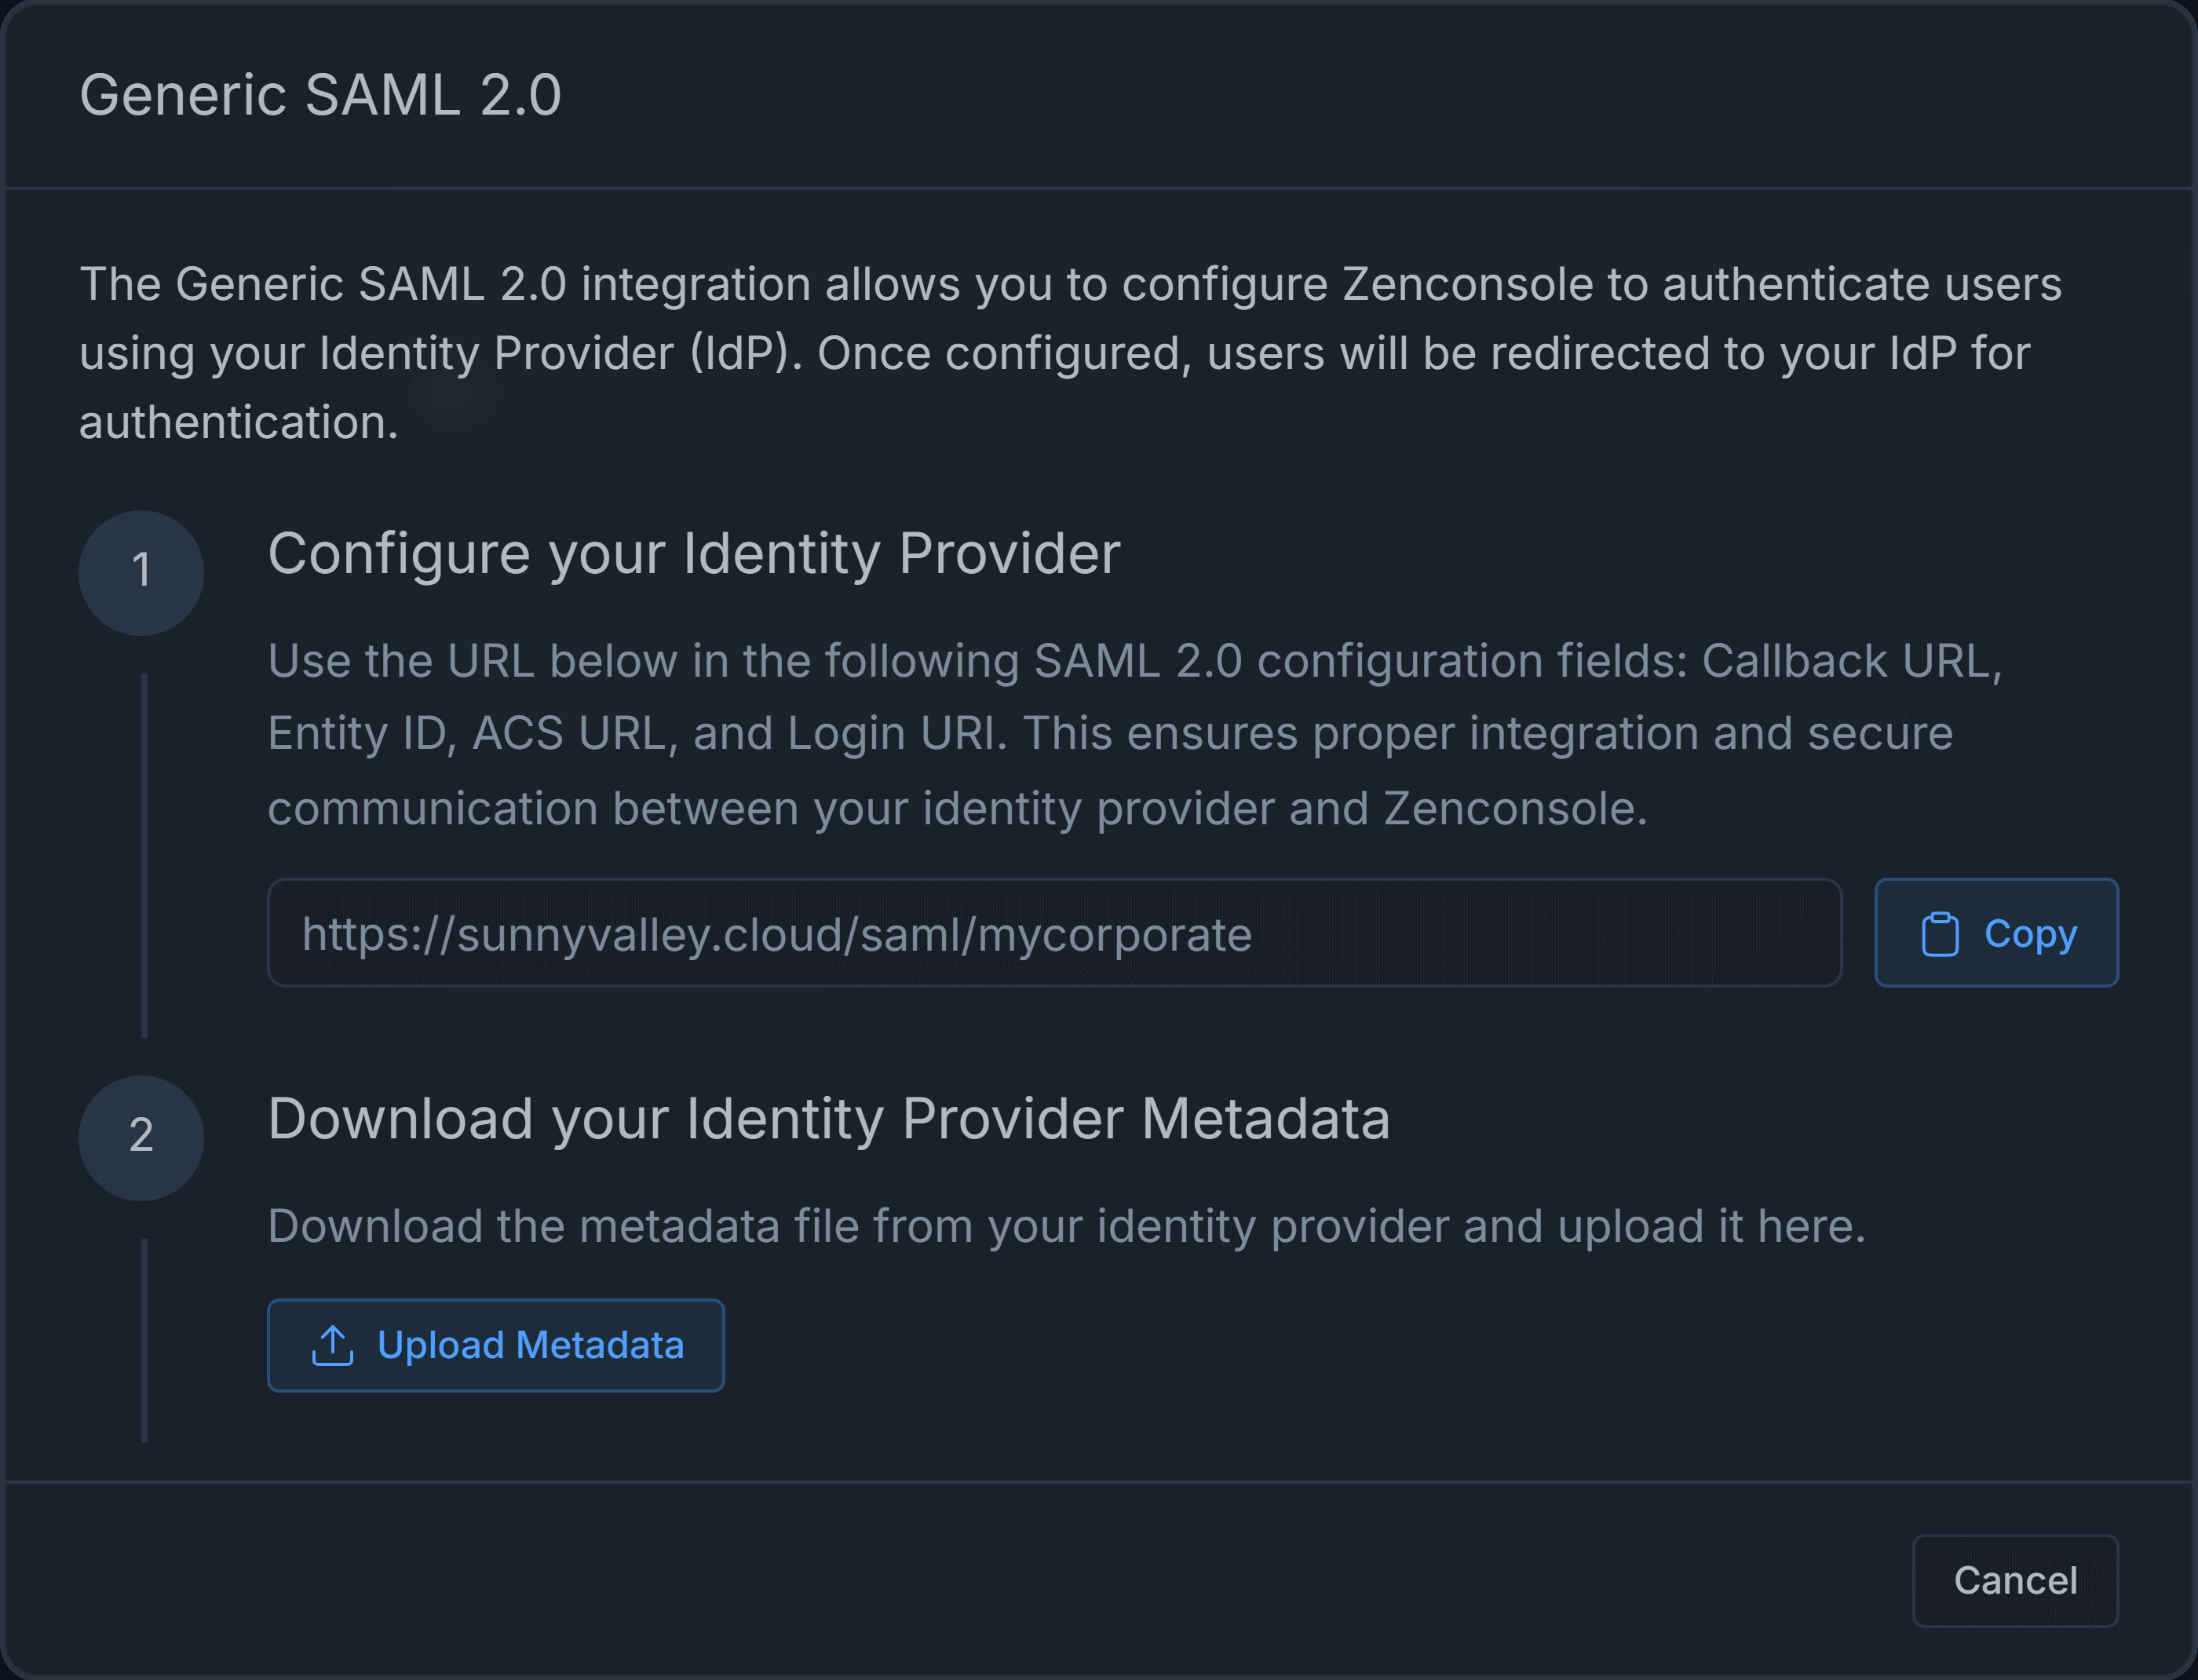
Figure 29. Configure SAML
-
You may copy the URL supplied in the window and integrate your identity provider and Zenconsole if you have not already done so.
-
Click Upload Metadata button to upload IdP metadata file. This will open file browser.
-
Select xml metadata file you have recently downloaded from identity provider and then click Open. This will upload the metadata file used for the SAML 2.0 integration.
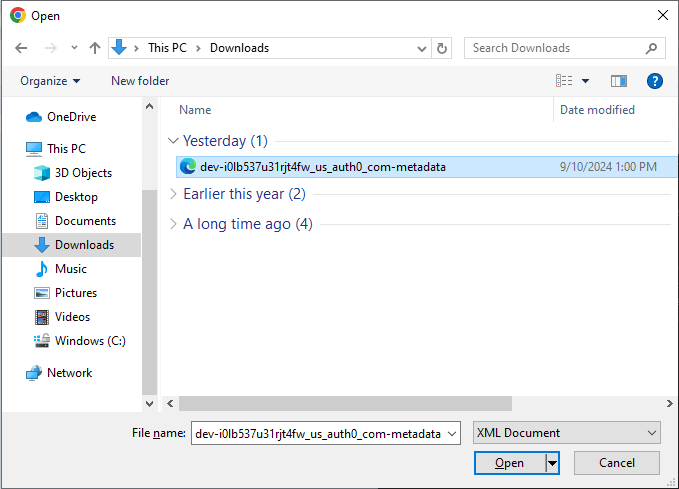
Figure 30. Selecting Metadata File
-
Click the Save Configuration button below to save the configuration and enable SAML 2.0 integration. Once the configuration is saved, the SAML 2.0 integration will be default authentication method for all users in this organization.

Figure 31. Enabling SAML Integration
-
You may check the Identity Provider (IdP) URL and Certificate Expiration date in the Generic SAML 2.0 configuration window.
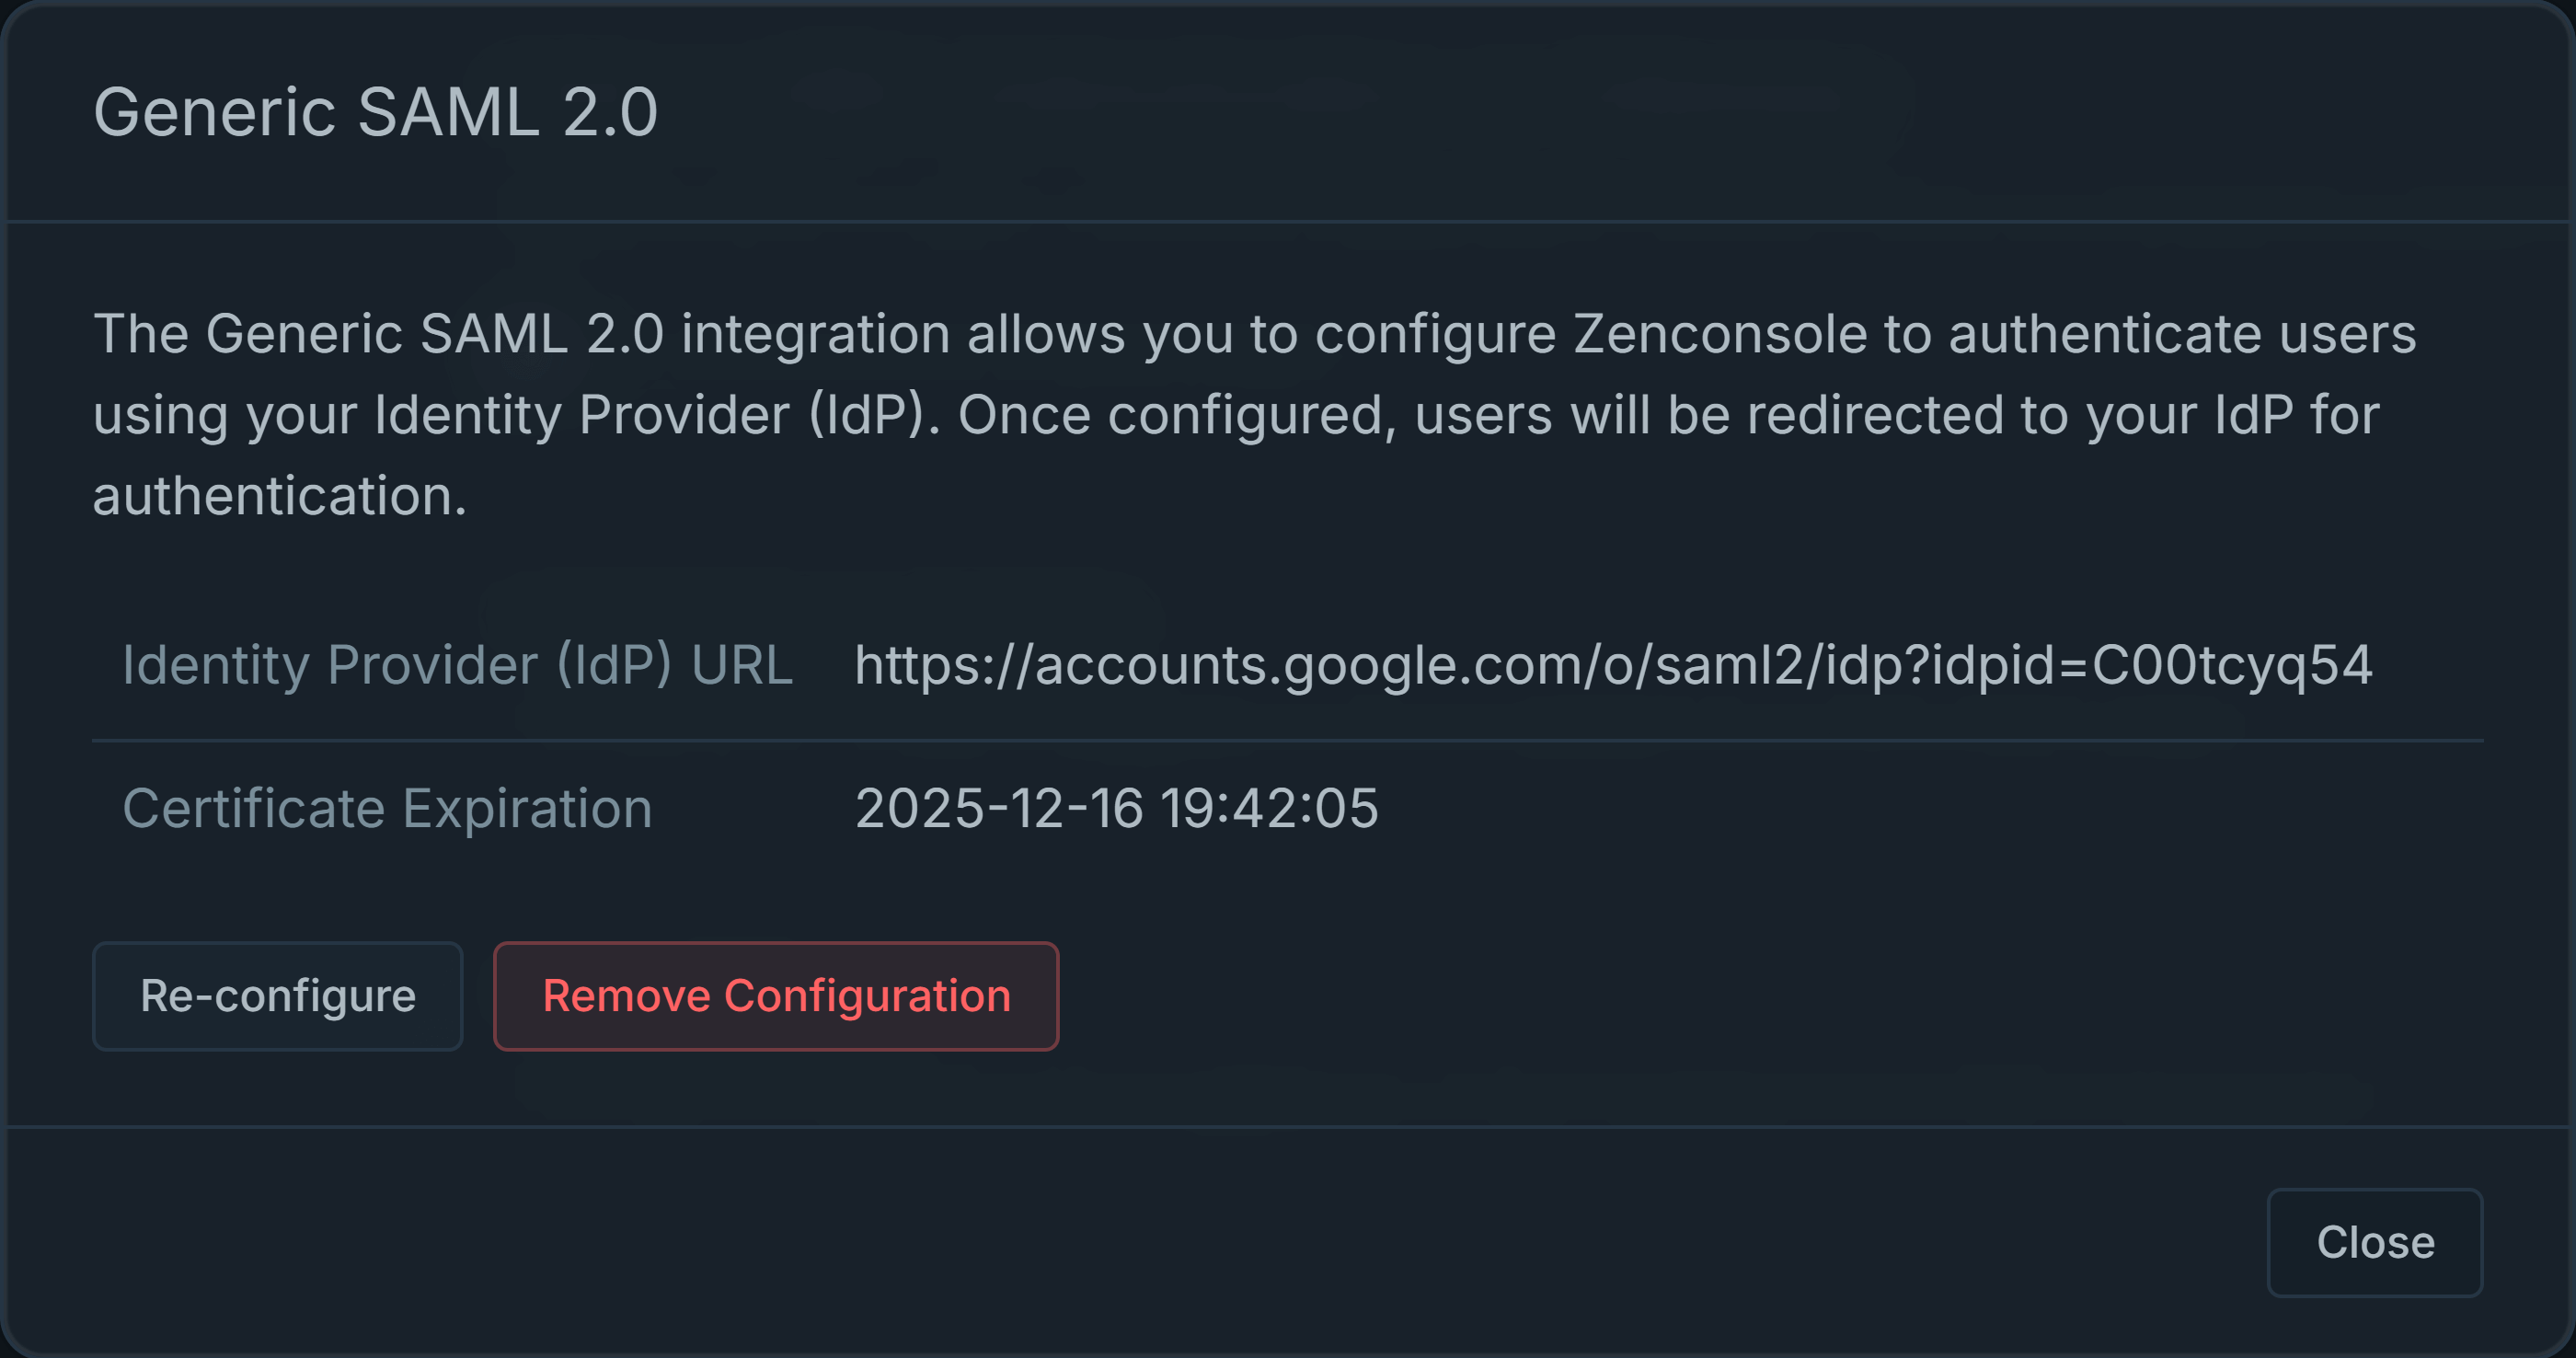
Figure 32. Generic SAML Configuration Completed
-
Click Close to complete the generic SAML2 configuration.
-
Now, you will see that SAML 2.0 is configured as the default authentication method for your organization.
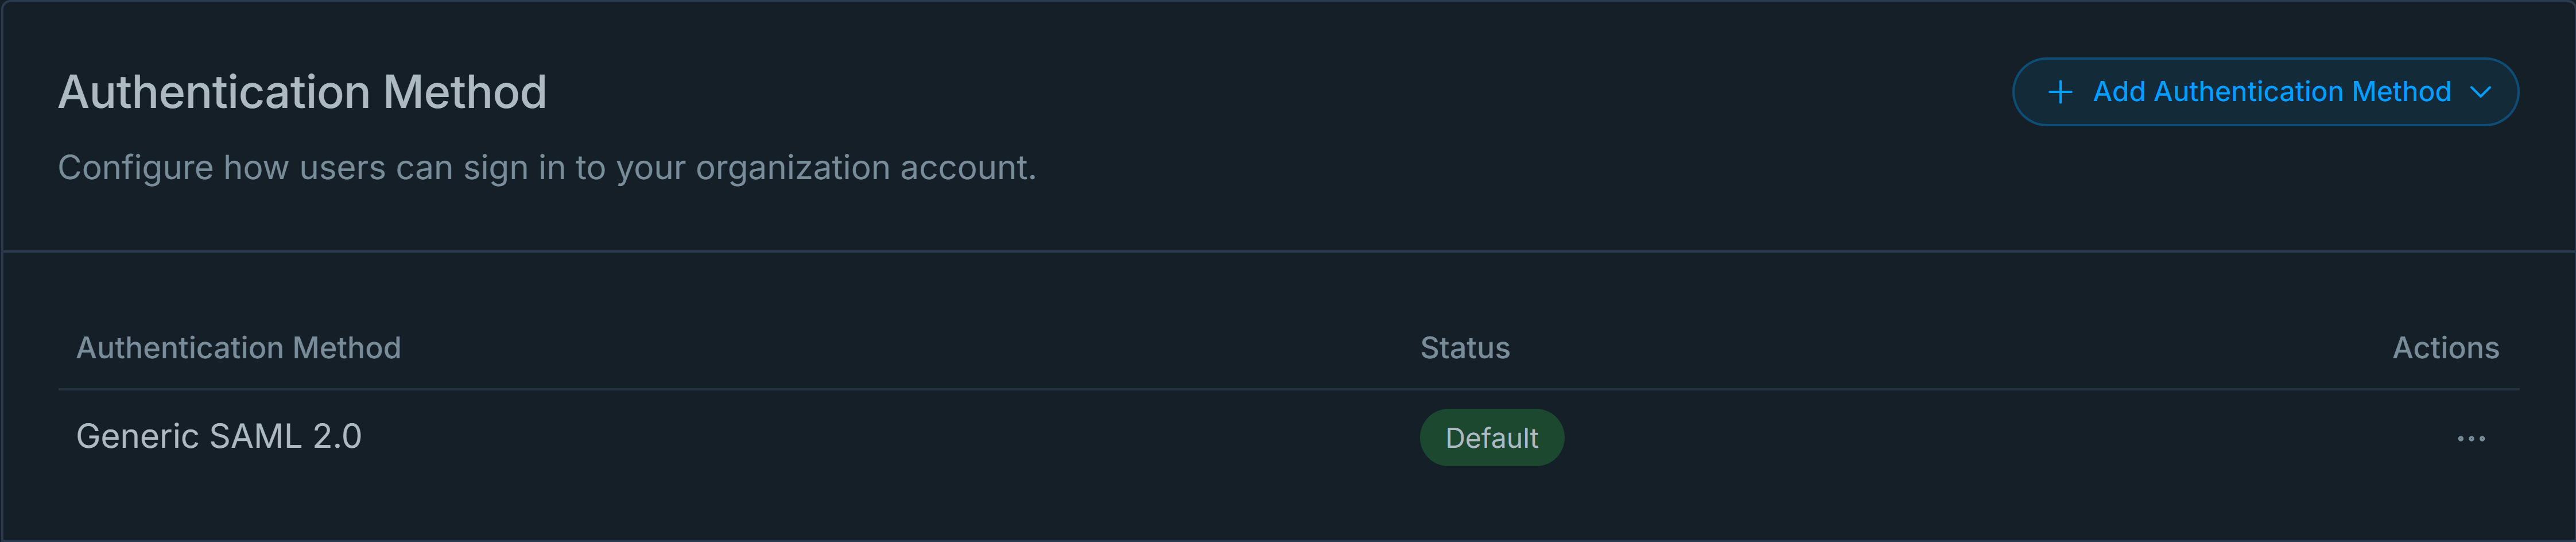
Figure 33. IAM Settings with-SAML Enabled
After enabling SAML 2.0 authentication method for your organization, do not forget to add users via the Users settings page. Otherwise, you may not be able to define user-based policies, or endpoints can not sign into the organization.
Enabling Local Account Authentication
Local Account Authentication allows organization administrators to create local user accounts using email addresses and passwords without requiring email verification. These accounts are isolated to the organization.
You can enable Local Account Authentication for your organization by following the steps below:
- Sign in to Zenconsole.
- Select the organization you want to manage.
- Navigate to Settings → Organization Settings → IAM → Identity & Access Management.
- Go to the Authentication Method section.
- Click the + Add Authentication Method dropdown menu in the upper-right corner.
- Select Local Account Authentication from the available authentication methods. The Local Account Authentication Configuration window appears.
- In the Configure Accepted Domains section, enter the email domain you want to allow for creating local user accounts in the Accepted domain field, such as
example.com. - Click + Add Domain to add the specified domain. Repeat this step to add additional domains if needed.
- Click Continue to complete the initial configuration.
- Review the configured domains in the Accepted Domains section. You can add additional domains using + Add Domain or remove an existing domain by clicking the x icon next to its name.
- Click Close to complete the process.
Once configured, Local Account Authentication appears in the Authentication Method list on the Identity & Access Management page.
Local accounts are specific to the organization and do not require email verification. Unlike Google Cloud Identity, Local Account Authentication does not automatically synchronize users and groups from an external identity provider.
Adding Local Account Authentication does not automatically change the organization's default authentication method. You can set it as the default authentication method separately if needed.
Enabling Microsoft Entra ID (Azure AD)
To use Microsoft Entra ID (formerly Azure AD) for identity management in your organization, you must integrate your Zenconsole organization with Microsoft Entra ID. This integration ensures that your organization's users and groups are automatically added and updated through regular synchronization, keeping information accurate and up to date without manual effort.
You can enable Microsoft Entra ID (Azure AD) for your organization and allow users to sign in using their Microsoft Entra ID accounts by following the steps below.
-
Login Zenconsole.
-
Select the organization you want to manage.
-
Navigate to the Settings → Organization Settings → IAM → Identity & Access Management page.
Figure 34. Identity & Access Management page
-
Go to Authentication Method pane at the top of the page.
-
Click + Add Authentication Method drop-down menu at the top right of the pane. All supported authentication methods will appear.

Figure 35. Selecting Azure for Authentication Method
-
Select Microsoft Entra ID (Azure AD) to configure it as an authentication method for your organization. This opens the configuration wizard.
-
Type the domain that you want to be synchronized with Zenconsole for user authentication. Users with email addresses from these domains can sign in to your organization.
-
Click + Add Domain button. You may add as many domains as you need. Accepted domains will be automatically displayed below. You may quickly remove them by clicking the
xicon next to the domain name if you need. -
Click Continue to proceed with the Azure AD configuration. This will provide a link for the Azure AD integration and await authorization from your domain administrator.
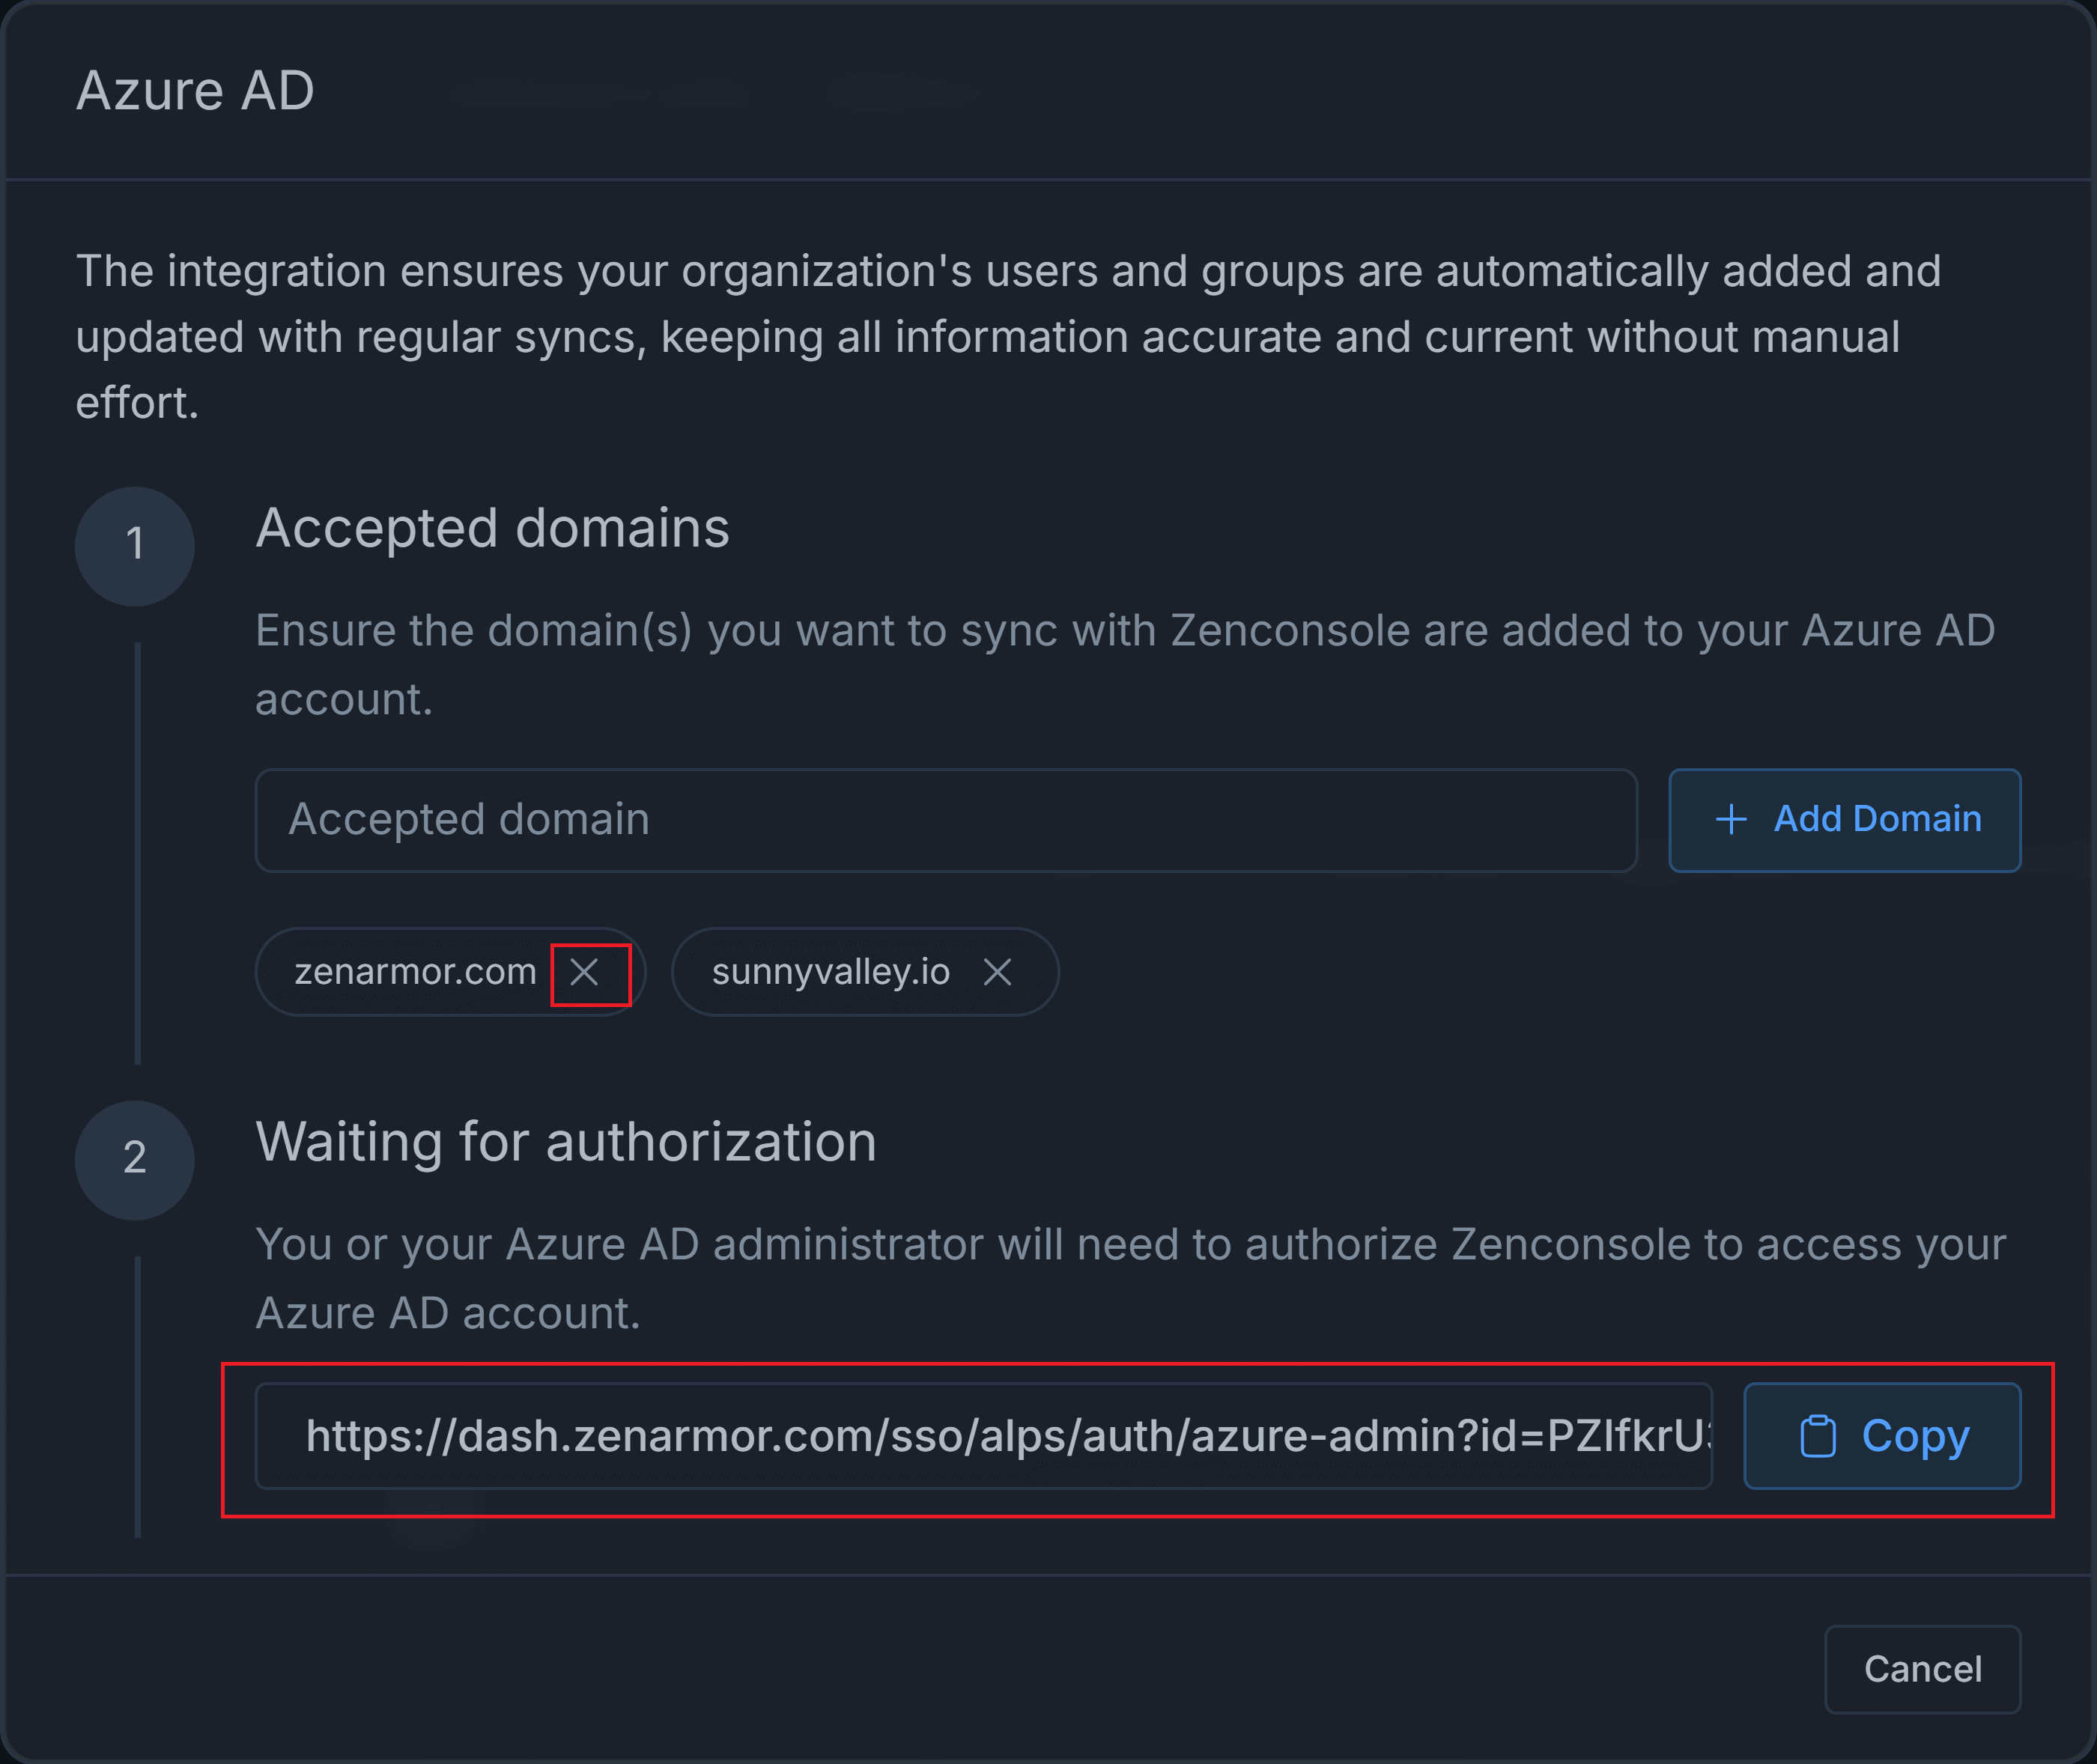
Figure 36. Adding Accepted Domains and Waiting for Microsoft Entra ID (Azure AD)
-
Select Microsoft Entra ID (Azure AD) to configure it as an authentication method for your organization. This opens the configuration wizard.
-
Open the generated link and sign in to Microsoft using an account with the required administrator privileges.
-
Click Accept to give the required privileges on your domain to Zenconsole.
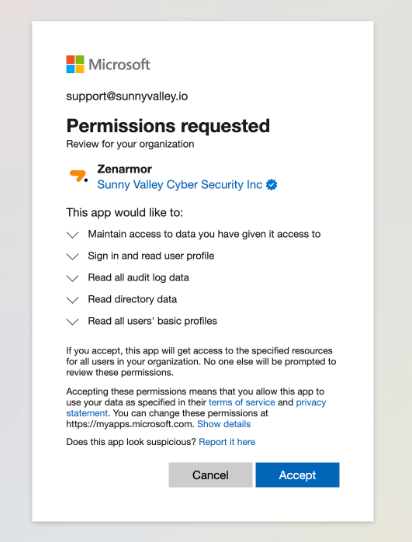
Figure 37. Accepting Permission Requests
-
You should observe that Zenconsole access has been granted to your domain. Zenconsole will now routinely update your users and groups, as they are now synchronized.
Figure 38. Google Access Granted
-
Click on the Zenconsole link which will redirect you to the organization Identity & Access Management page. You should see that Microsoft Entra ID (Azure AD) in the Authentication Method list.
Beware that to let your domain users sign in to the organization, you will need to approve them by navigating to the Users settings page.
Even if you enable Microsoft Entra ID (Azure AD) as an authentication method in your organization, it's important to enforce Single Sign-On (SSO) authentication. This is necessary in order to view the usernames of users who connect to the network through a gateway, such as OPNsense or pfSense software, in your reports.
Reconfiguring Authentication Methods
You may easily update your existing authentication methods by following the next steps.
-
Login Zenconsole.
-
Select the organization you want to manage.
-
Navigate to the Settings → Organization Settings → IAM → Identity & Access Management page.
-
Go to Authentication Method pane at the top of the page.
-
Click the Actions menu with 3-dot
...icon next to the authentication method that you want to reconfigure. This will open a drop-down menu.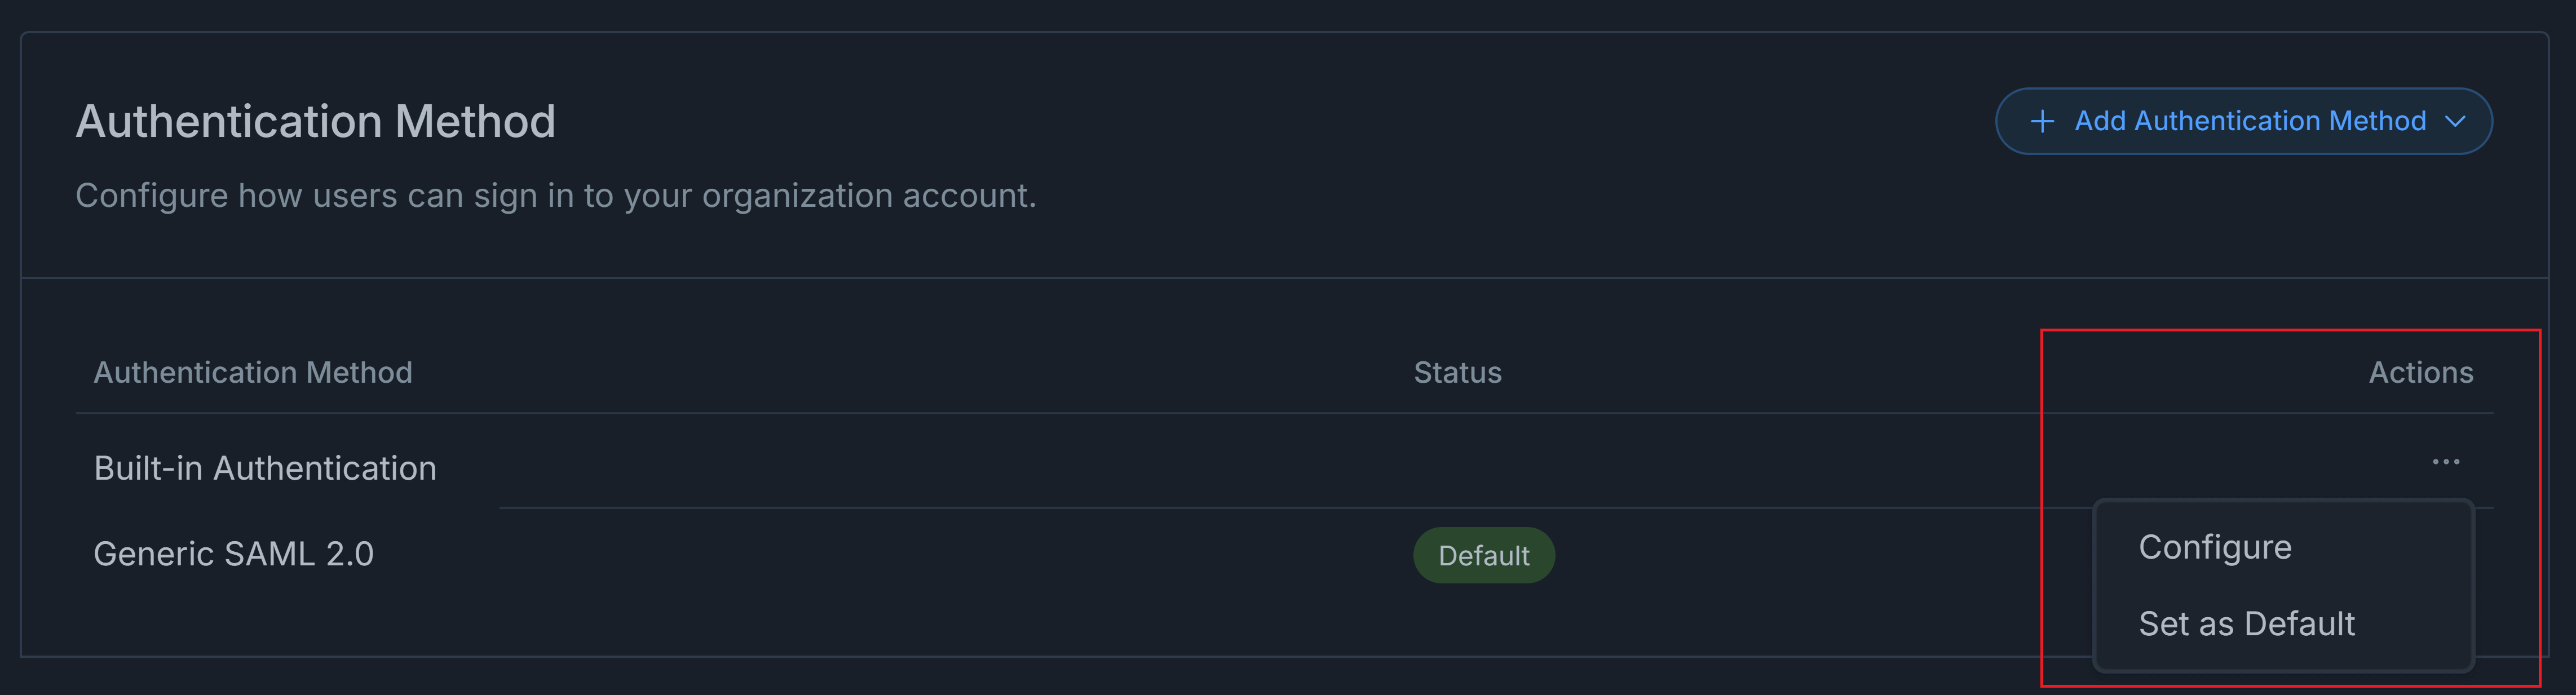
Figure 39. Authentication Method Actions
-
Click Configure menu to update settings. This will open authentication configuration window.
Figure 40. Reconfiguring Authentication Methods
-
Click Reconfigure button.
-
Upload new metadata by clicking on the Upload Metadata button.
-
Click Save Configuration button to save the new configuration.
-
Click Close.
Removing Authentication Methods
You may easily delete your existing authentication methods by following the next steps.
-
Login Zenconsole.
-
Select the organization you want to manage.
-
Navigate to the Settings → Organization Settings → IAM → Identity & Access Management page.
-
Go to Authentication Method pane at the top of the page.
-
Click the Actions menu with 3-dot
...icon next to the authentication method that you want to remove. This will open a drop-down menu. -
Click Configure menu to update settings. This will open the authentication configuration window.
Figure 41. Removing Authentication Methods
-
Click Remove Configuration button. A notification will appear to confirm the removal.
-
Click Remove to delete the authentication method.
Setting Default Authentication Methods
You may easily change the default authentication method if you have multiple methods by following the next steps.
-
Login Zenconsole.
-
Select the organization you want to manage.
-
Navigate to the Settings → Organization Settings → IAM → Identity & Access Management page.
-
Go to Authentication Method pane at the top of the page.
-
Click the Actions menu with 3-dot
...icon next to the authentication method that you want to set as default. This will open a drop-down menu.Figure 42. Setting Default Authentication Methods
-
Click Set as Default menu to update settings. A notification will appear to confirm the new settings.
-
Click Set as Default to save the settings.
Video
Here is the hands on video for Zenarmor IAM Management feature.
Configuring the Reauthentication Interval
The Reauthentication Interval setting allows administrators to enforce periodic reauthentication for users during an active Zenarmor Endpoint Application session. When enabled, this feature ensures that users must periodically confirm their identity before continuing a session, improving session security and minimizing the risk of unauthorized access in shared or unattended environments.
By configuring this setting, organizations can align session behavior with internal security policies and regulatory compliance requirements. Periodic reauthentication helps ensure that user identity remains continuously validated throughout active sessions.
This setting is particularly valuable in environments where devices are shared, remote access is common, or sessions remain active for extended periods. In such cases, long-running sessions may become vulnerable to unauthorized access if left unattended or if session credentials are compromised.

Figure 43. Reauthentication Interval Page
You can configure the Reauthentication Interval setting through the Zenconsole management interface by following the steps below.
-
Login Zenconsole.
-
Select the organization that you want to manage.
-
Click Settings from the left sidebar menu.
-
Navigate to: Organization Settings → IAM → Identity & Access Management
-
Scroll down to the Reauthentication Interval section.
Figure 44. Reauthentication Interval Page
-
Toggle Enforce Periodic Reauthentication to ON.
-
Set the desired reauthentication interval (in days).
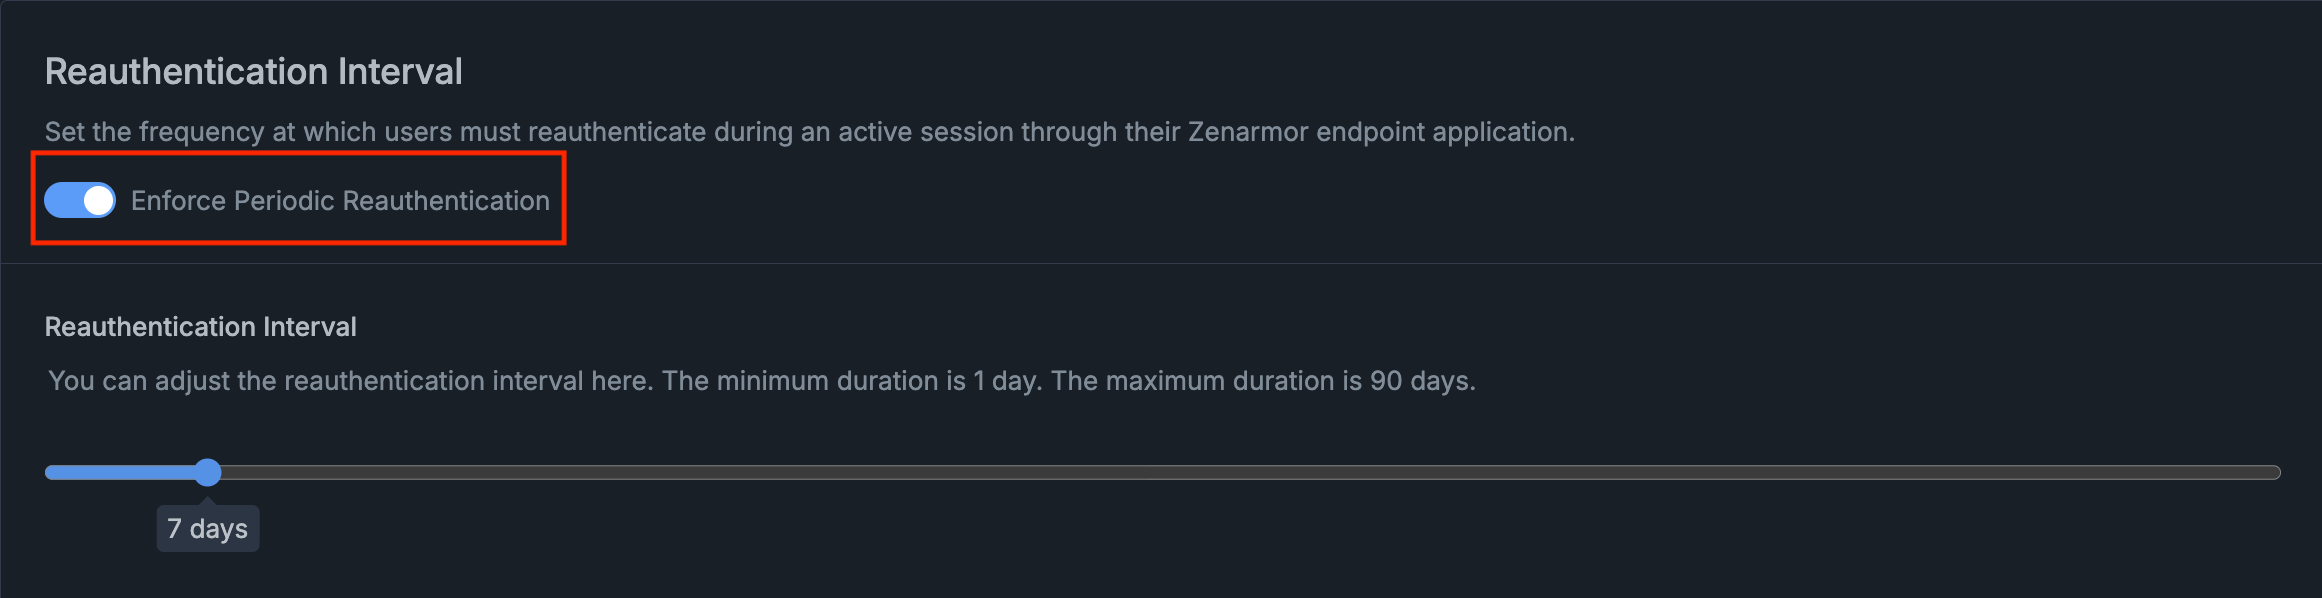
Figure 45. Configuring Reauthentication Interval
The interval must be between 1 and 90 days****.
-
After saving the configuration, a confirmation notification appears in the lower-right corner of the screen. This message confirms that the new reauthentication interval has been successfully applied.

Figure 46. Session Expiry Updated Confirmation
Once enabled, users will be required to reauthenticate after the configured number of days.
Changing the Reauthentication Interval
To change an existing reauthentication interval, follow these steps:
- Navigate to the Reauthentication Interval section.
- Ensure that Enforce Periodic Reauthentication is enabled.
- Locate the Reauthentication Interval slider.
- Drag the slider to adjust the interval to the desired number of days.
The selected duration is displayed below the slider.
Disabling Periodic Reauthentication
To disable periodic reauthentication, follow these steps:
- Navigate to the Identity & Access Management page.
- Locate the Reauthentication Interval section.
- Disable the Enforce Periodic Reauthentication toggle.
Once disabled, the reauthentication interval setting is hidden, and periodic reauthentication is no longer enforced through this feature.