Managing Organization DNS Settings on Zenconsole
Zenarmor supports Split DNS within Zero-Trust networks, allowing administrators to define custom internal DNS servers and domains for their secure environments. This capability enables organizations to manage internal and external DNS resolution independently, providing greater security, privacy, and control over how domain names are resolved.
With Split DNS, internal resources such as intranet portals, file servers, and internal APIs can be resolved within the organization's secure environment, while public domains continue to use external DNS resolvers.
This dual-resolution capability helps prevent the exposure of internal DNS information, improves name resolution performance, and ensures consistent DNS behavior across distributed networks.
Zenconsole allows administrators to perform the following DNS management operations:
-
Configure internal DNS servers and domains for Zero-Trust networks.
-
Add multiple DNS servers to a domain.
-
Configure preferred DNS settings for Windows Active Directory registration.
-
Edit, reorder, and delete existing DNS configurations.
-
Synchronize DNS configuration changes across applicable instances.
-
Re-synchronize DNS settings on endpoint devices when necessary.
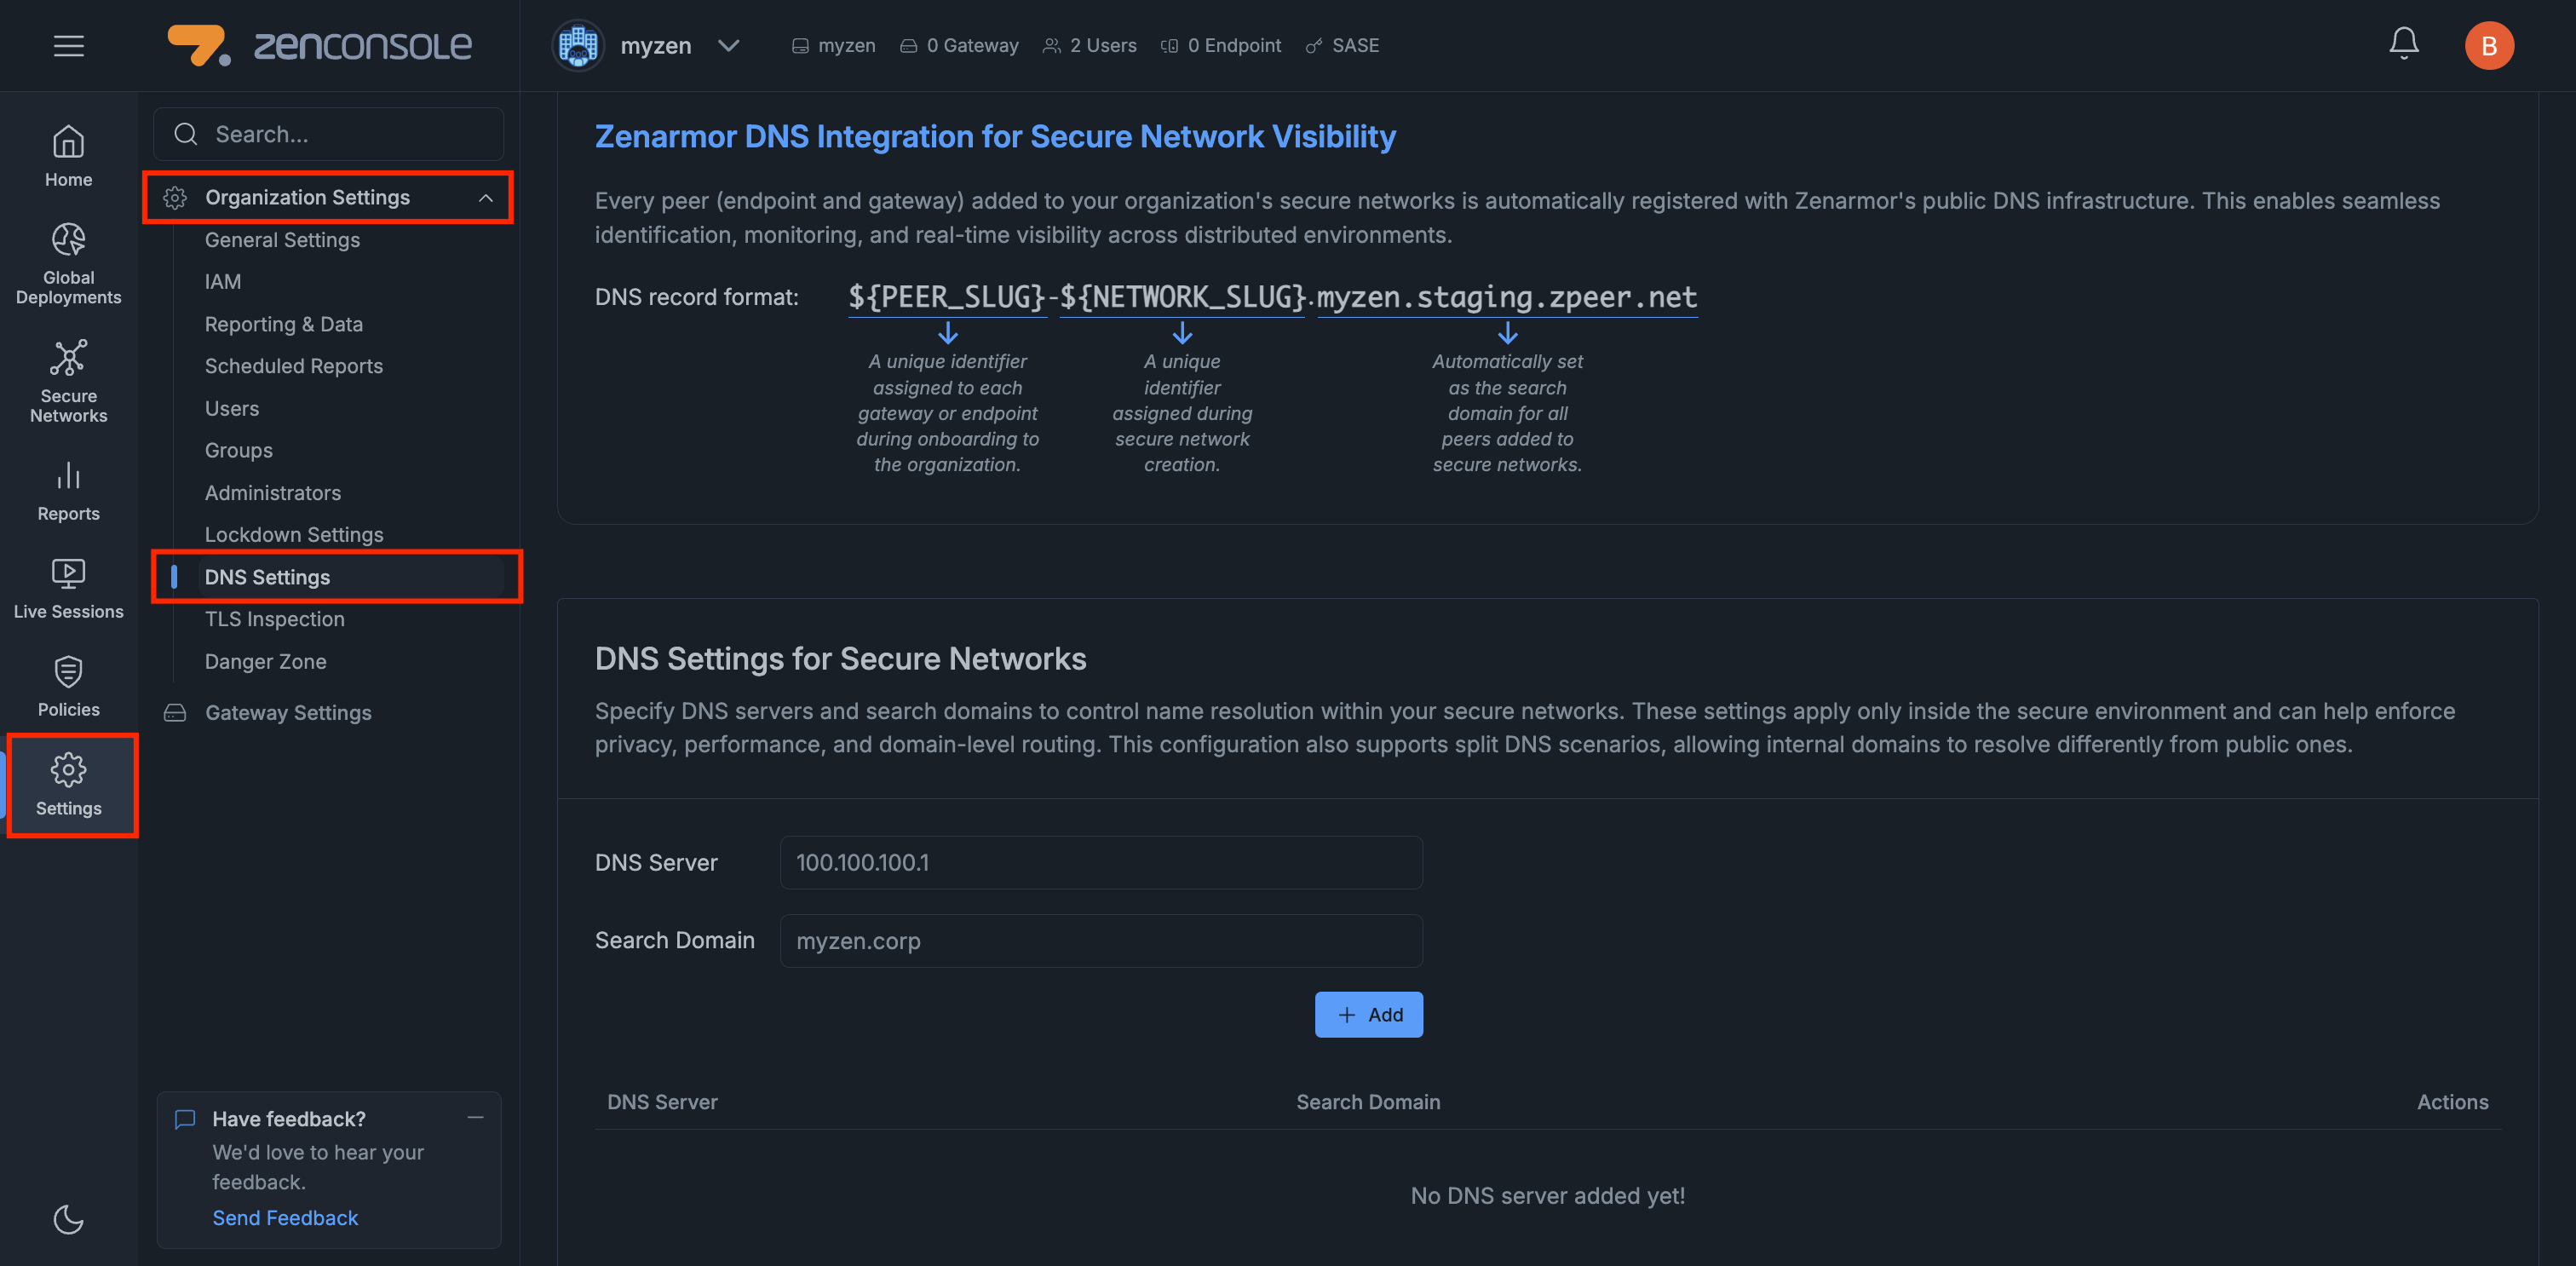
Figure 1. Organization DNS Settings on Zenconsole
Core Components of Zenarmor's Split DNS
Zenarmor's Split DNS capability is built upon an integrated DNS infrastructure that automatically registers and maintains network peers and their associated DNS records.
This architecture ensures that gateways and endpoints within Zero-Trust networks can be consistently identified and resolved through Zenarmor's DNS infrastructure, providing a reliable foundation for secure and context-aware name resolution.
The capability consists of two primary components.
1. Zenarmor DNS Integration for Zero-Trust Network Visibility
Every peer (gateway or endpoint) added to an organization's Zero-Trust networks is automatically registered within Zenarmor's public DNS infrastructure.
This process enables seamless peer identification, monitoring, and real-time visibility across distributed environments.
Each peer is assigned a unique DNS record following the naming convention displayed in the Zenarmor DNS Integration for Zero-Trust Network Visibility section:
${PEER_SLUG}-${NETWORK_SLUG}.<DNS_DOMAIN>
This structure provides a consistent naming convention for peers and networks managed within the organization.
It also simplifies network diagnostics and supports reliable name resolution across distributed environments.

Figure 2. Zenarmor DNS Integration and DNS Record Format
2. DNS Settings for Zero-Trust Networks
The DNS Settings for Zero-Trust Networks section allows administrators to specify DNS servers and domains that control name resolution within their Zero-Trust networks.
These settings apply only within the secure environment and support Split DNS configurations, enabling internal domains to resolve differently from public domains.
Administrators can:
- Assign internal DNS servers to specific domains.
- Configure multiple DNS servers for a single domain.
- Manage domain-specific name resolution.
- Specify preferred DNS settings for Windows Active Directory registration.
- Reorder domains and DNS servers.
For example, a query to intranet.myzen.corp can be resolved through an internal DNS server such as 100.100.100.1, while a query to google.com continues to use an external DNS resolver.
This separation helps organizations maintain privacy, optimize DNS performance, and control how internal resources are accessed.

Figure 3. DNS Settings for Zero-Trust Networks
Configuring DNS Settings for Zero-Trust Networks
To access and configure DNS settings for your organization's Zero-Trust networks, follow the steps below:
- Log in to your Zenconsole account.
- Select the organization you want to configure.
- Navigate to Settings → Organization Settings → DNS Settings from the left-hand navigation menu.
The DNS Settings page allows you to configure internal DNS servers and domains, manage DNS resolution, and specify Active Directory DNS registration preferences within your Zero-Trust networks.
Adding a DNS Server and Domain
To add a DNS server and domain configuration, follow the steps below:
-
Navigate to Settings → Organization Settings → DNS Settings from the left-hand navigation menu.
-
Locate the DNS Settings for Zero-Trust Networks section.
-
Configure the following fields:
- DNS Server: Enter the IP address of your internal DNS server, such as
10.10.10.10. - Domain: Enter the internal domain name that should be resolved through the specified DNS server, such as
sunnyvalley.corp. - Use this nameserver/suffix for AD DNS registration (Windows): Enable this option if you want to use the specified DNS server and domain suffix for Windows Active Directory dynamic DNS registration.
- DNS Server: Enter the IP address of your internal DNS server, such as
-
Click + Add to save the configuration. The newly added domain and DNS server appear in the DNS settings table.
-
After the configuration is saved, Zenconsole displays a confirmation notification. You can click Sync Now to synchronize the changes immediately or wait for the next automatic synchronization cycle, which occurs every 15 minutes.

Figure 4. Adding DNS Servers and Domains
Enabling Use this nameserver/suffix for AD DNS registration (Windows) specifies the DNS server and domain suffix to be used for Windows Active Directory dynamic DNS (DDNS) registration, including A/AAAA records and, when applicable, PTR updates.
If multiple domain/DNS configurations are defined, only the entry with this option enabled is used for Active Directory DNS registration. Other entries are used for name resolution only.
You can configure multiple domains and assign one or more DNS servers to each domain. Additional DNS servers can be added to an existing domain using + Add DNS Server in the DNS settings table.
Adding Multiple DNS Servers to a Domain
Zenconsole allows you to configure multiple DNS servers for the same domain, providing flexibility and supporting redundant DNS infrastructure.
To add another DNS server to an existing domain, follow the steps below:
- Navigate to Settings → Organization Settings → DNS Settings.
- Locate the domain you want to configure.
- Click + Add DNS Server in the DNS Servers column.
- Enter the IP address of the additional DNS server.
- Confirm the addition.
The new DNS server appears alongside the existing DNS servers associated with the domain.

Figure 5. Adding Multiple DNS Servers to a Domain
Reordering Domains and DNS Servers
Zenconsole allows you to change the order of configured domains and DNS servers using drag and drop.
To reorder the entries, follow the steps below:
- Navigate to Settings → Organization Settings → DNS Settings.
- Locate the domain or DNS server you want to reposition.
- Drag and drop the entry to the desired position.
- Verify that the entries appear in the intended order.
Managing Existing DNS Configurations
Zenconsole allows administrators to manage previously configured DNS entries directly from the DNS settings table.
Editing an Existing Domain
To modify an existing domain name, follow the steps below:
-
Navigate to Settings → Organization Settings → DNS Settings.
-
Locate the domain you want to modify.
-
Click the Edit (pencil) icon in the Actions column.

Figure 6. Editing an Existing Domain
-
In the Edit Domain dialog box, update the domain name.
-
Click Save to apply your changes.

Figure 7. Edit Domain Dialog
A success notification confirms that the configuration has been updated.
Removing a DNS Server from a Domain
You can remove an individual DNS server without deleting the entire domain configuration.
To remove a DNS server, follow the steps below:
-
Navigate to Settings → Organization Settings → DNS Settings.
-
Locate the domain containing the DNS server you want to remove.
-
Find the corresponding DNS server in the DNS Servers column.
-
Click the X icon next to its IP address.

Figure 8. Removing a DNS Server from a Domain
-
In the Warning dialog box, review the confirmation message indicating that the selected DNS server IP address definition will be removed from the domain.
-
Click Remove to confirm the operation, or Cancel to keep the existing configuration.
The selected DNS server is removed from the domain configuration.
Before removing a DNS server, ensure that the remaining DNS configuration can continue resolving the required internal domains.
Deleting a Domain Configuration
To delete an existing DNS configuration, follow the steps below:
-
Navigate to Settings → Organization Settings → DNS Settings.
-
Locate the domain you want to delete.
-
Click the Delete (trash) icon in the Actions column.

Figure 9. Deleting a Domain Configuration
-
In the Warning dialog box, review the confirmation message indicating that the domain definition and all its DNS server entries will be removed.
-
Click Remove to confirm the deletion, or Cancel to keep the existing configuration.
The selected domain and its associated DNS server entries are removed from the DNS settings table.
Re-Synchronizing DNS Settings on Endpoint Devices
DNS settings are automatically synchronized to endpoint devices when they are added to an organization and whenever DNS-related configuration changes occur.
However, if the DNS settings on an endpoint device become corrupted or inconsistent, administrators can manually initiate a re-synchronization.
To re-synchronize DNS settings, follow the steps below:
- Navigate to Settings → Organization Settings → DNS Settings.
- Locate the Re-Sync DNS Settings button in the upper-right corner of the DNS Settings for Zero-Trust Networks section.
- Click Re-Sync DNS Settings.
- In the Re-Sync DNS Settings confirmation dialog box, review the information provided.
- Click Proceed to initiate the re-synchronization process.
Alternatively, click Cancel to close the dialog box without proceeding.

Figure 10. Re-Synchronizing DNS Settings on Endpoint Devices
DNS settings are synchronized automatically under normal conditions. The manual Re-Sync DNS Settings option is intended for situations where endpoint DNS settings need to be restored or refreshed.